Execute routine and large-scale changes while maintaining governance, resilience, and security.
Feel Like Every Change Is a Guessing Game?
IP Fabric contextualizes every change in an application-aware model of cloud and network behavior, so you and your AI agents can understand how any change will impact critical services before you make it.
Installing new servers? How many interfaces do we have free? What are capabilities? Do they meet PCI hardware requirements? We can quickly look at a chart, pull out an export, and be done.
Get Complete Visibility Before & After Changes
Automatically run pre / post-change snapshots to:
- Model every device and dependency across network, cloud, and host layers
- Run any custom security, regulatory, or operational checks across millions of infrastructure data points
- Detect any unauthorized or unplanned changes
- Track milestones for large-scale projects
Automate Change Workflows
Eliminate manual verification and human error by automatically:
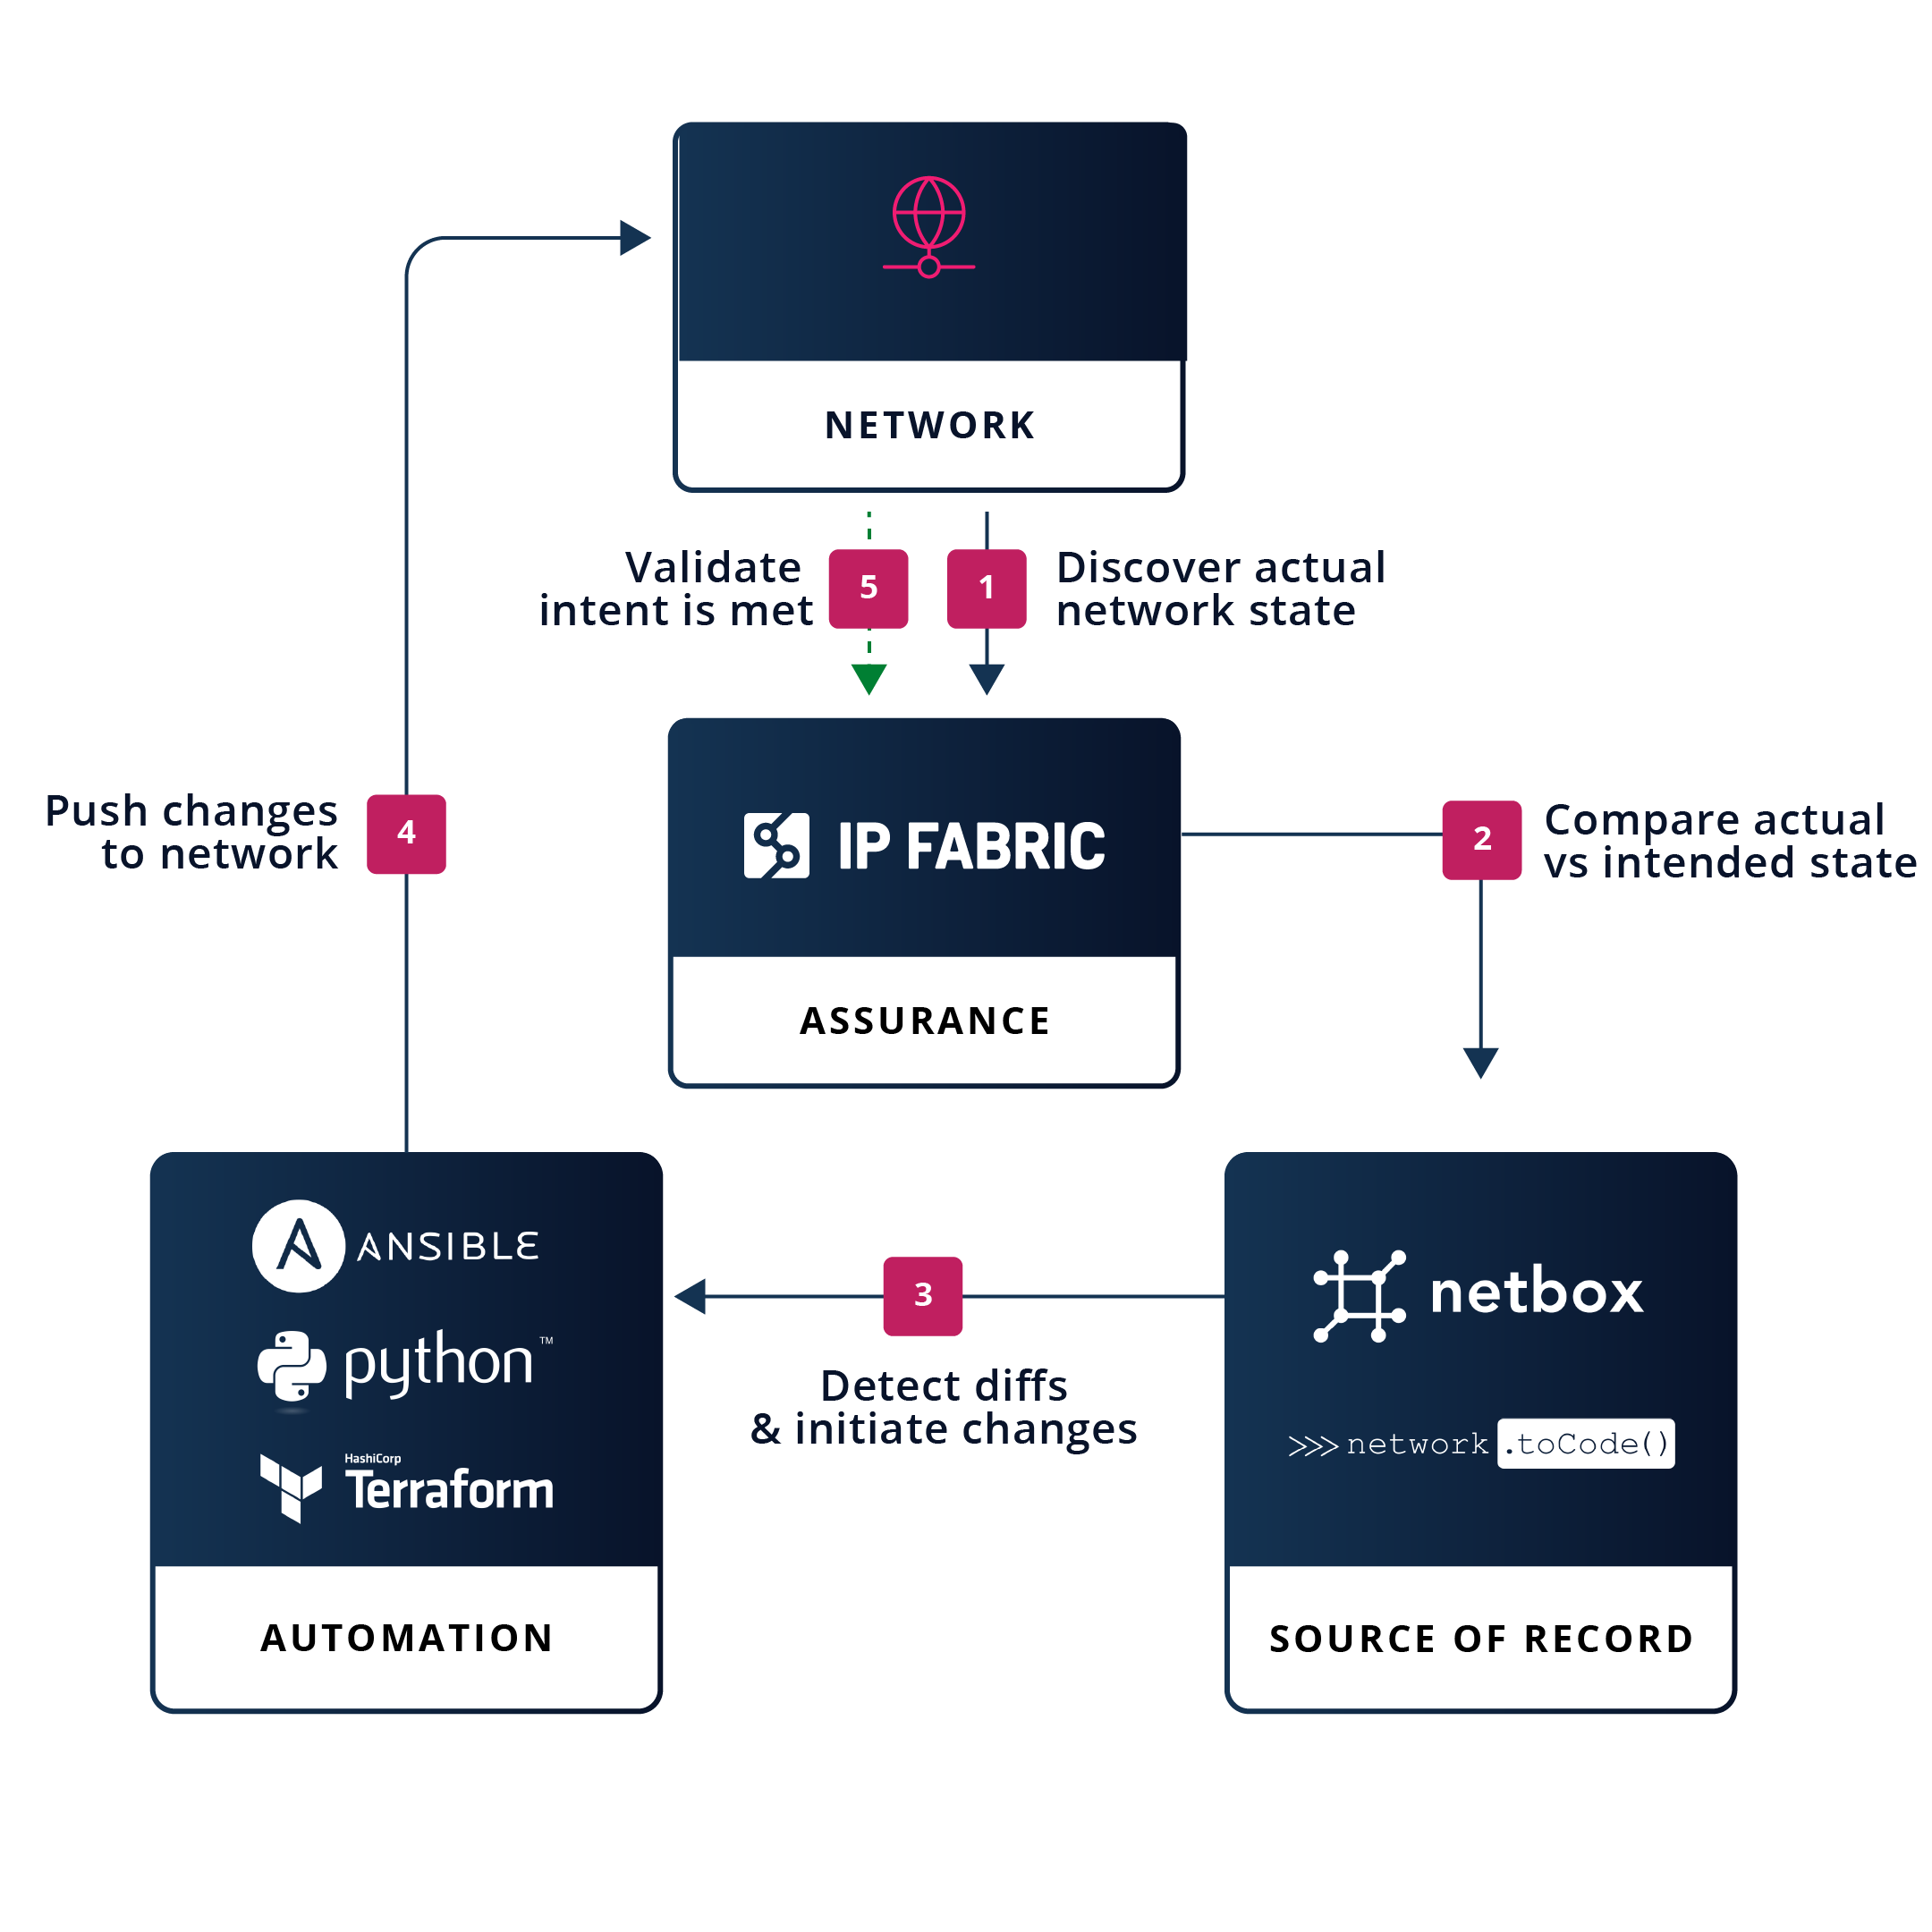
- Syncing with NetBox to detect any drift between observed network behavior and intent
- Populating ServiceNow tickets with implementation plans, risk & impact analyses, and more
- Sending webhooks to Ansible to activate change management playbooks while maintaining proper Separation of Duties (SoD)
Reduce The Risk Of Outages & Rollbacks
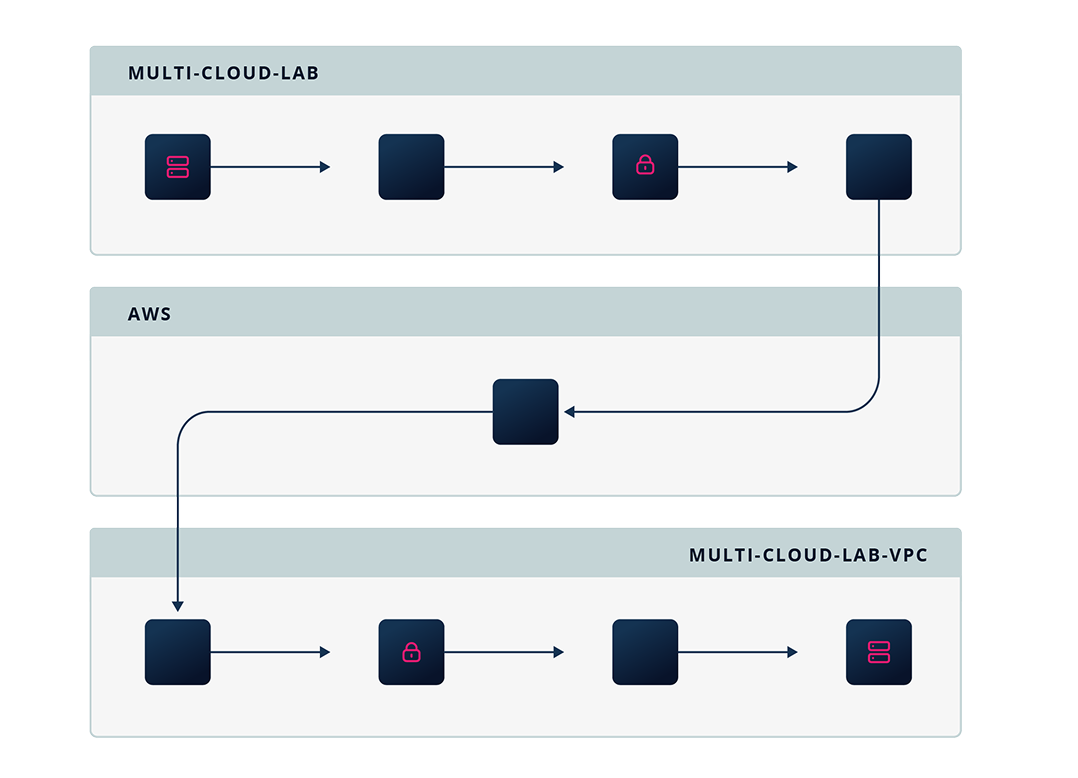
Run “what-if” scenarios and end-to-end path lookups with the MCP server to:
- Identify the blast radius of any change before you make it
- Validate your intent against observed cloud & network behavior
- Get timestamped proof that security & regulatory controls are implemented according to intent
Resources

Webinar
Modernize Change Management
Automate changes from troubleshooting to post-change resolution.

Demo Video
Run “What-If Scenarios” With IP Fabric’s MCP Server
Simulate a “what-if” failover simulation on a real traffic path, grounded in observed cloud and network behavior.

Blog
Level Up NetBox Automation In 5 Easy Steps
Build a more resilient, secure, and compliant network with IP Fabric’s NetBox plugin.
FAQs
IP Fabric builds a full inventory of every cloud and on-prem device in your environment using read-only credentials. This inventory includes device hostnames, serial numbers, model numbers, lifecycle status, performance, utilization, and more. See the full list of device attributes in our supported features matrix.
IP Fabric simulates the behavior of your on-prem and cloud environments, and models any dependencies that involve your critical applications. This process only takes a few minutes, which means you can generate several snapshots per day, and use them to track your progress during a change window. These snapshots also serve as timestamped proof of continuous compliance.
IP Fabric’s end-to-end path lookup feature shows the entire path that a given packet traverses through network, cloud, and host layers. Simply add a source and a destination for your path, and you’ll see an end-to-end map of the devices, dependencies, and configurations that are implicated in your change. You can also run “What-If” scenarios to anticipate the effect a change will have before you make it.
IP Fabric is a read-only platform, and does not automatically push changes in order to maintain a Separation of Duties (SoD), which is essential for proper governance.
However, IP Fabric does initiate the change management process by automatically populating ITSM tickets with deterministic insights, and sending webhooks to automation tools like Ansible. IP Fabric also tracks the progress of any change by taking snapshots during your change management window. Lastly, it’ll validate that your change was implemented correctly by syncing your latest IP Fabric snapshot against your source of intent (e.g. NetBox).
Yes. If IP Fabric detects that your network is deviating from business intent, it can initiate the change management process by generating a justification, implementation plan, risk and impact analysis, rollback plan, and test plan. This can easily be inputted into ServiceNow or your ITSM of choice.
See IP Fabric in Action
Our expert team is here to help you get started.