Understand the risks and opportunities in new networks, or prove separation from the ones you’re no longer managing.
Discovering a New Network From Scratch?
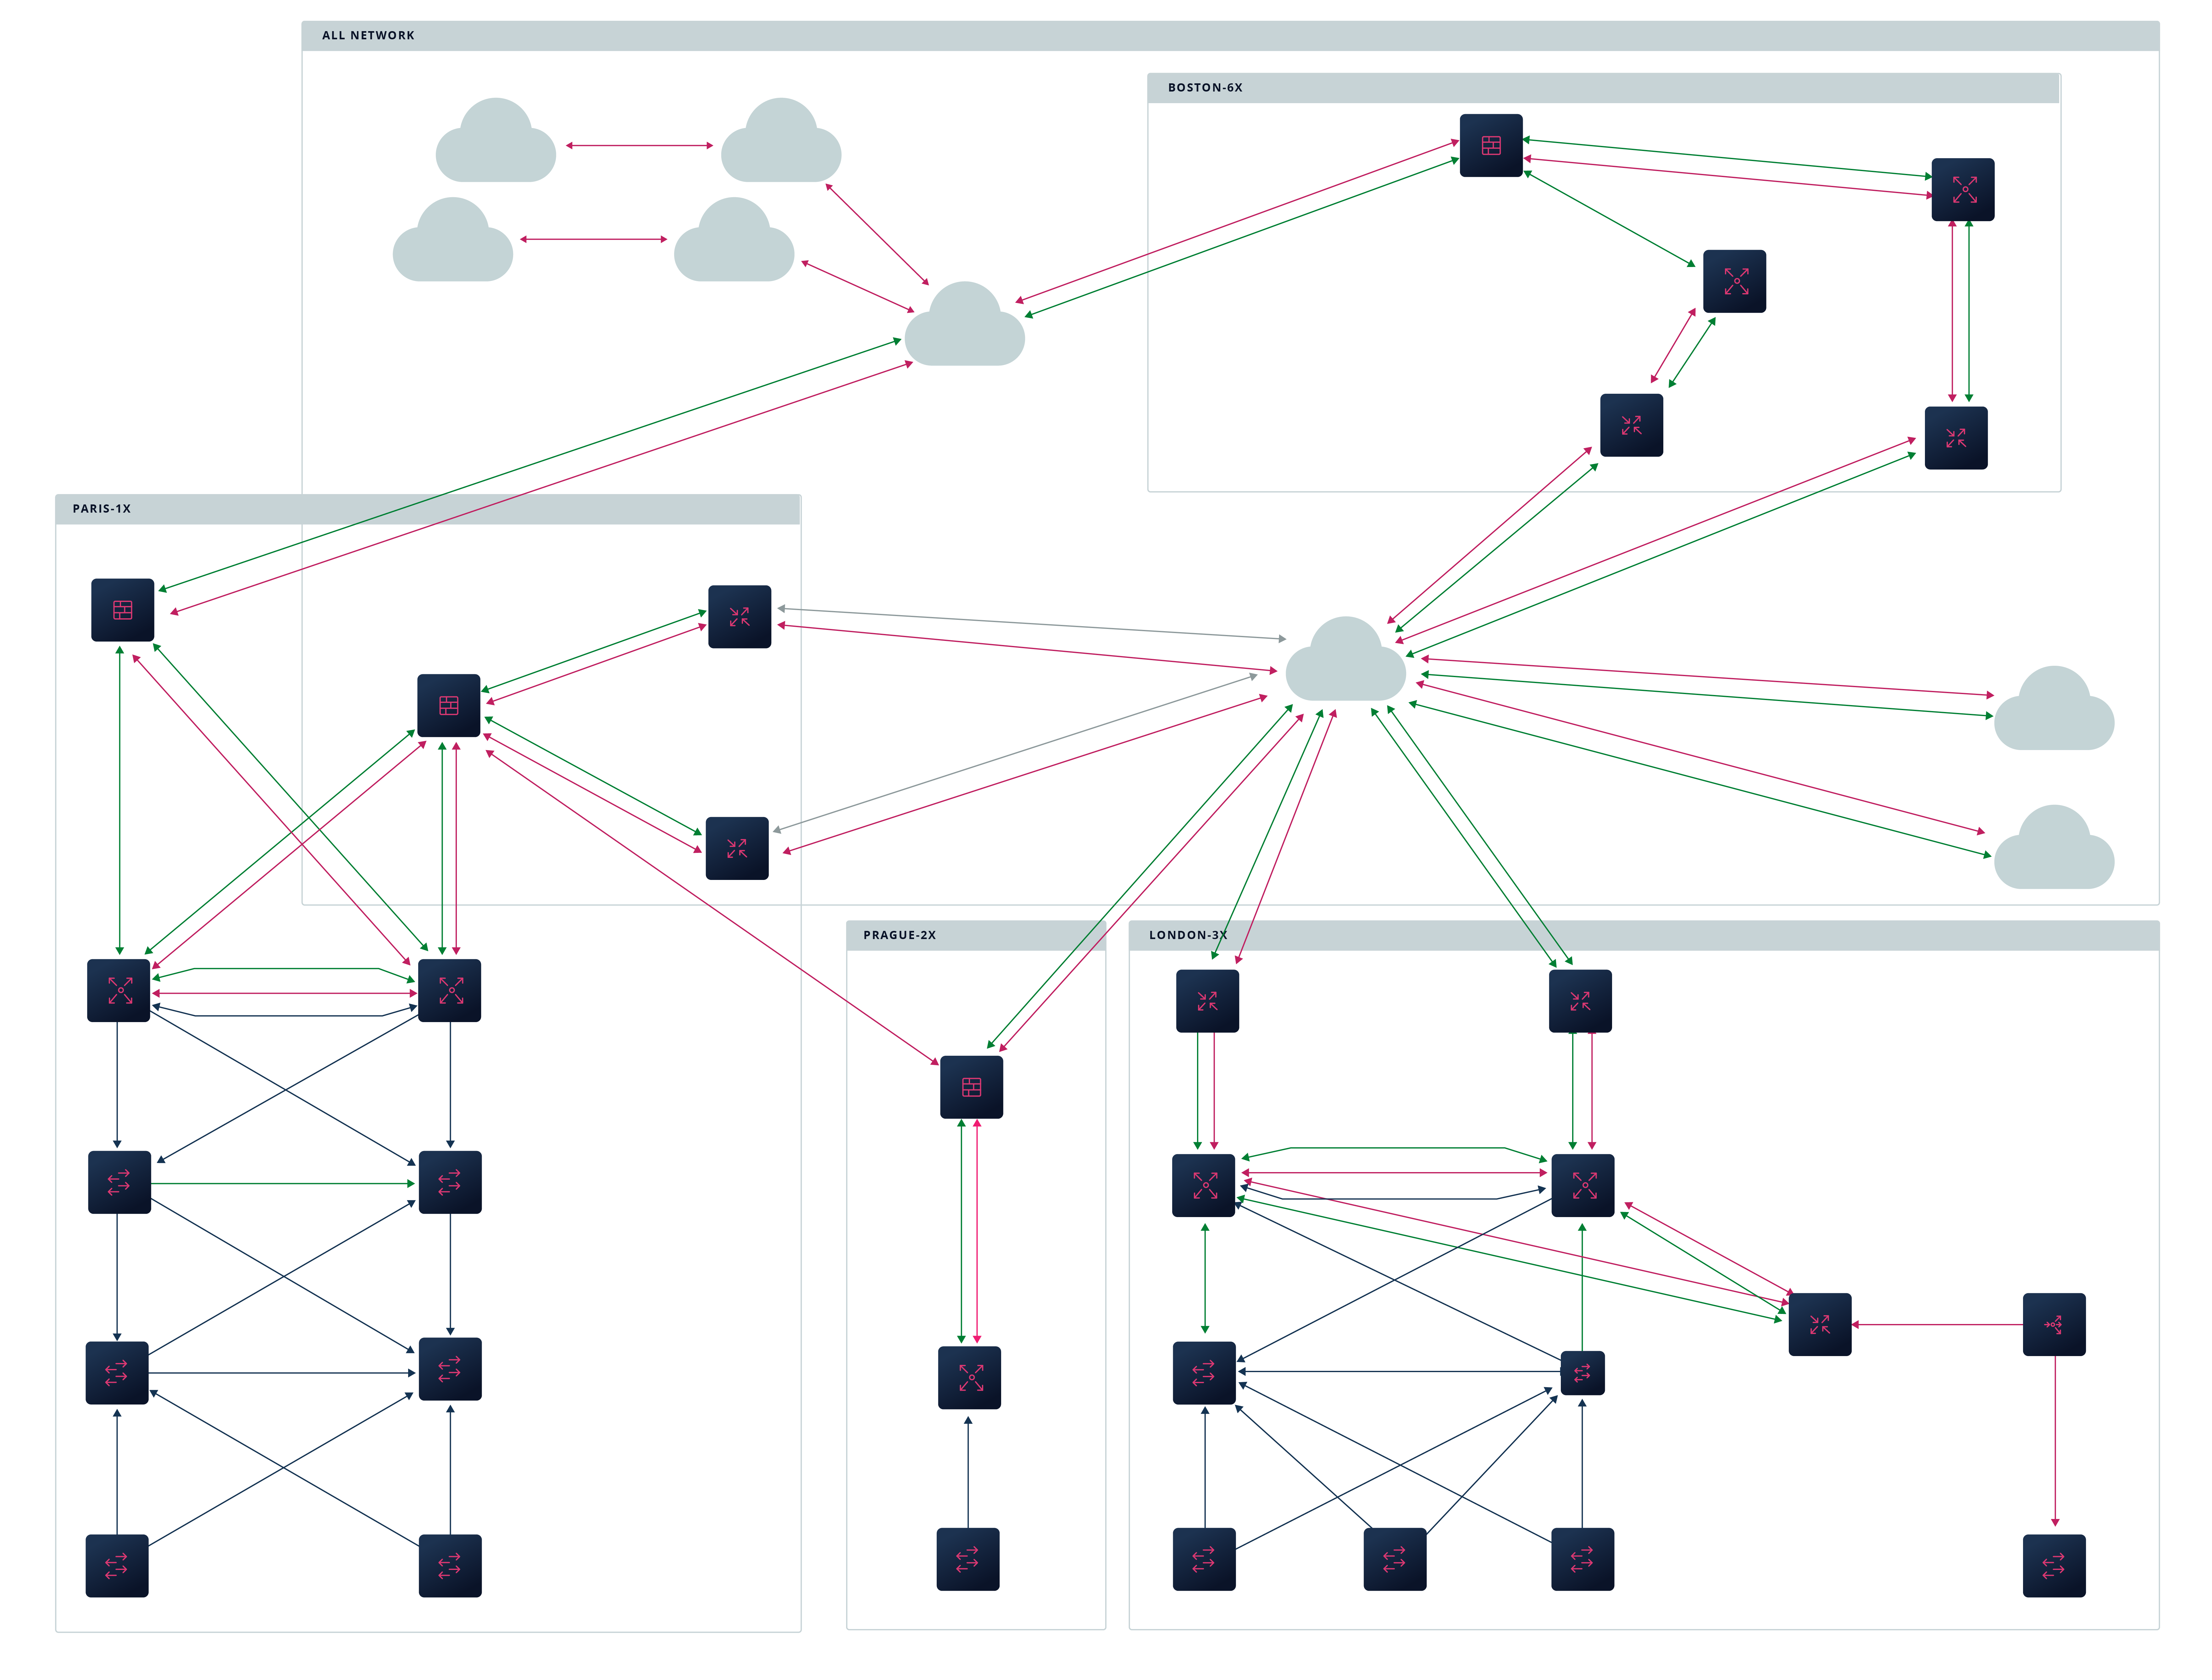
M&As leave behind a patchwork of inherited designs and inconsistent documentation. But IP Fabric can document new networks and map critical dependencies in minutes.
New engineers can use IP Fabric’s dynamic diagrams to view the network as a whole and understand the privacy policies we have in our network.
Get a Baseline of Network Behavior
Build an interactive digital twin of every device, connection, and configuration in your environment. Map on-prem devices and cloud objects directly to applications and critical services.
Secure Every New Device & Connection
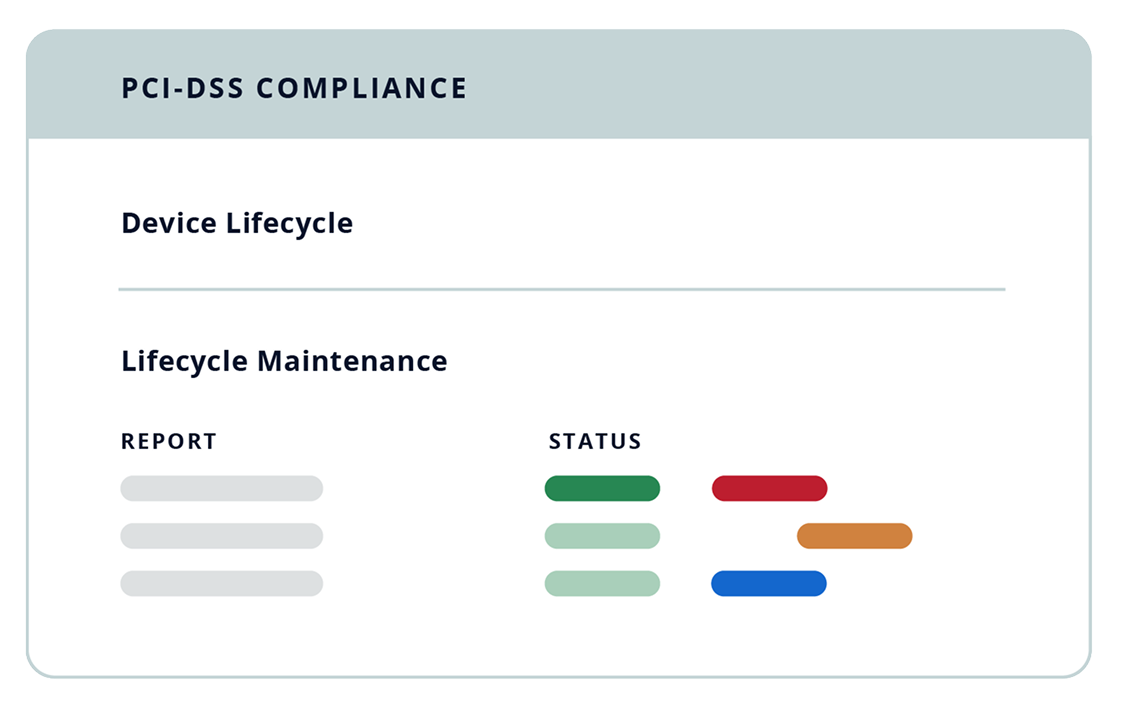
Get a complete and normalized understanding of your acquired environment in minutes, so you can onboard employees and remediate any risks to security / regulatory compliance.
Eliminate Unnecessary Spend
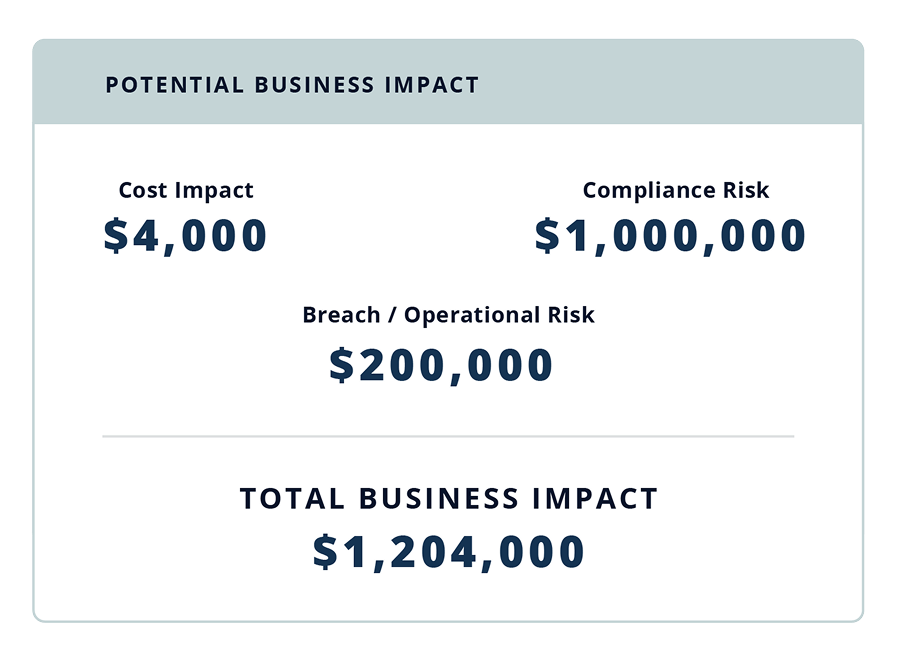
Optimize your budget by pinpointing duplicate licensing, parallel support contracts, and hardware that’s no longer in production.
Resources

Demo Video
Run “What-If” Scenarios With IP Fabric’s MCP Server
Simulate a “what-if” failover simulation on a real traffic path, grounded in observed cloud and network behavior.

Blog
Improve Network Visibility in Hybrid Multi Cloud Environments
Unify insights across hybrid multi cloud environments.
Demo Video
Simplify M&As With Network Assurance
Automatically discover, map, and document newly acquired networks in minutes instead of months.
FAQs
IP Fabric discovers network and cloud devices through CLI commands and API calls using read-only credentials, then identifies neighboring devices until 100% of them are found. From there, it creates a vendor-neutral digital twin of your actual cloud and network behavior at that point in time, complete with native Layer 1–Layer 3 topologies. This is distinct from tools that rely on Simple Network Management Protocol (SNMP) for discovery, as they can’t always discover all on-prem / cloud vendors or map Layer 2–Layer 3 topologies. IP Fabric also layers on application data from external tools like Illumio, so you have a full picture of dependencies across cloud, network, and host layers.
After divesting a part of your network, you need to prove that the separation is complete. IP Fabric maps every device and dependency implicated in the divested network, so nothing gets missed in the handover. Once the divestiture is complete, you can run end-to-end path lookups to confirm that none of your devices or applications were affected in a way that introduces any risk. IP Fabric’s end-to-end snapshots also serve as timestamped proof of security and regulatory compliance throughout every stage of the divestiture process.
IP Fabric is vendor-agnostic. It discovers and normalizes data across all major vendors into a single interactive model, so an inherited Juniper environment is just as visible as your existing Cisco Meraki one. Visit our supported features matrix to learn more.
Most wasted spend hides in the parts of your network you can’t see. IP Fabric discovers every known and unknown device and dependency, so that you can identify wasted spend from underutilized devices, duplicate contracts, and more. Read about the “Hidden Bill of Bad Data” to learn how you can save on Operational Expenses (OpEx) and Capital Expenditures (CapEx).
In every snapshot, IP Fabric runs a series of pre-built and custom intent checks across millions of network data points. Pre-built checks are based on industry best practices, but it’s easy to create custom checks without any specialized query languages. The results of these checks are reported in a normalized, user-friendly dashboard, and can be accessed via IP Fabric’s open API and enterprise-grade MCP server.
See IP Fabric in Action
Our expert team is here to help you get started.