Use this interactive microsite to map security and regulatory controls to on-prem, cloud, and application environments.
Compliance Hub
Daily Discovery & Inventory
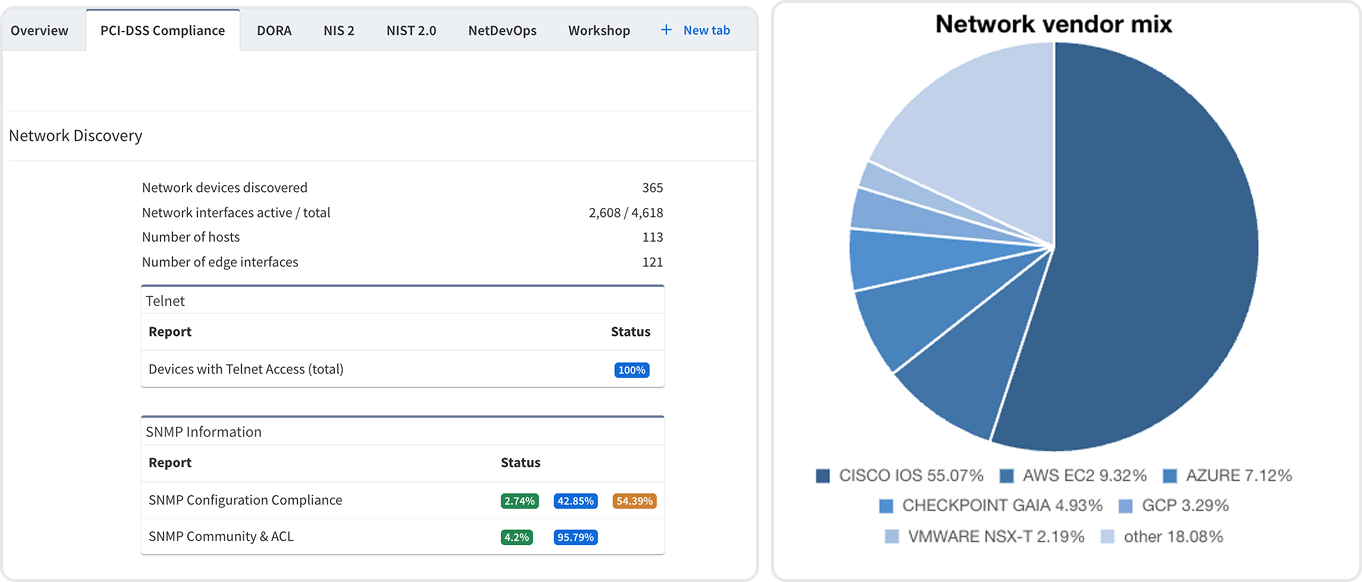
Network devices with Telnet access may represent a violation of PCI DSS (v4.0 – Requirement 2.2.6 & 8.2.2), which disallows use of insecure protocols unless justified and protected with compensating controls. Manually collecting and documenting this information is time-consuming and often inaccurate, leaving you subject to violations, and consequently, monetary and administrative penalties.
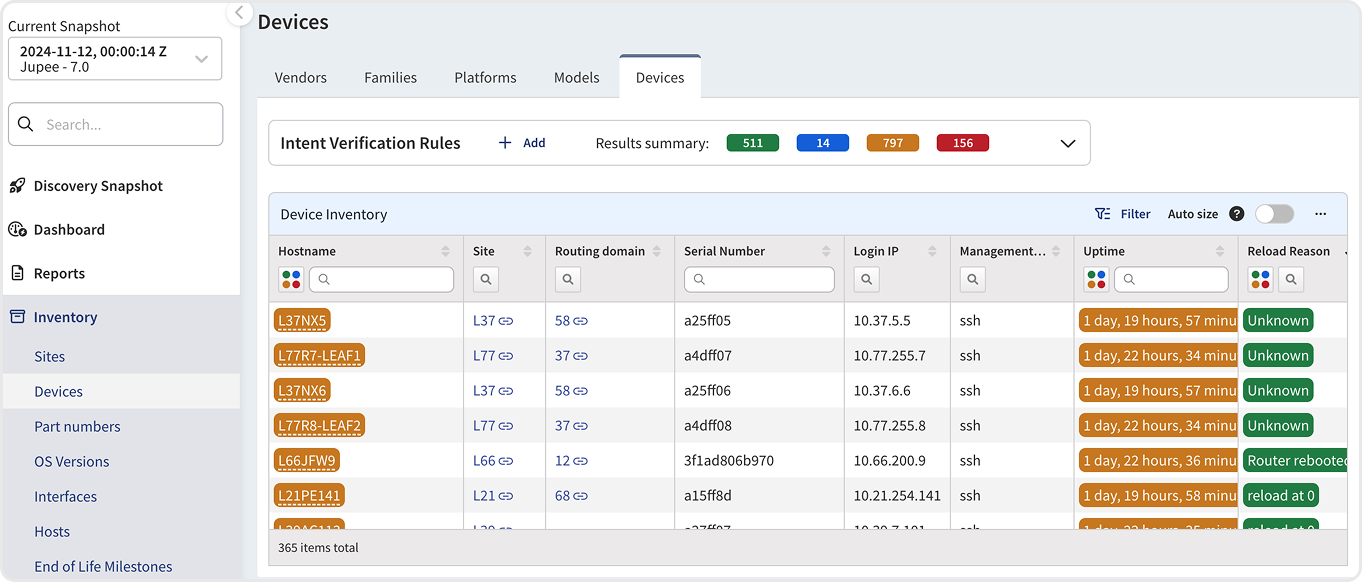
A fortified network device inventory represents the point-in-time “inventory of system” PCI requires.

More on PCI-DSS
Lifecycle Management
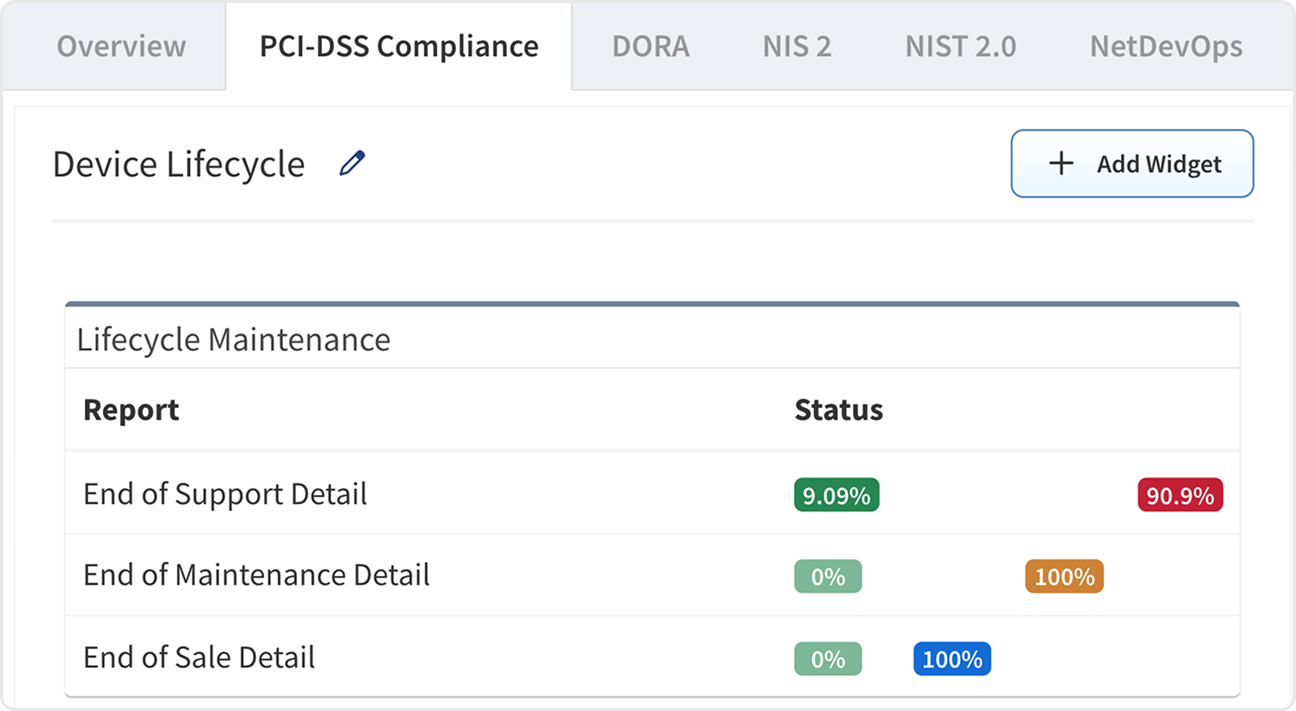
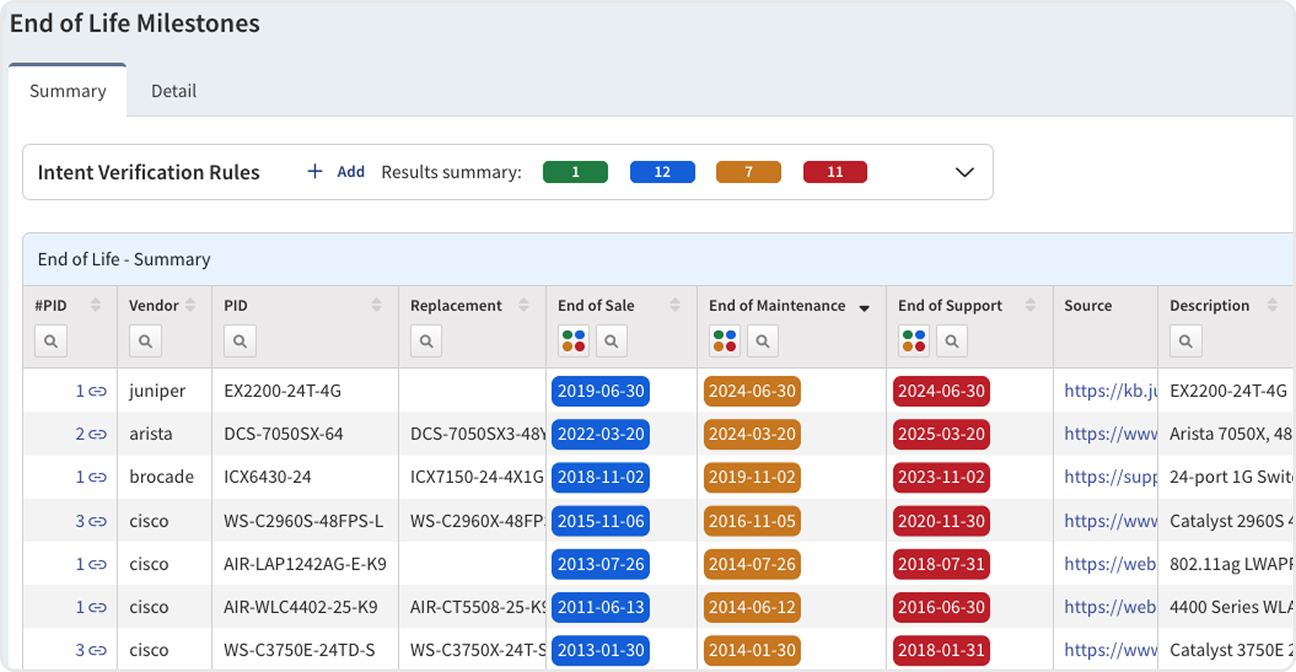
IP Fabric provides detailed Lifecycle Maintenance Information with every snapshot – automating collection and normalization of this data from disparate vendors and technologies ensures accurate planning, reporting, and operation of critical networks.
Devices that have reached end-of-life (EOL), end-of-maintenance, or end-of-support may no longer receive critical security updates, firmware patches, or vendor assistance, making them vulnerable to exploitation and non-compliant with most security standards. PCI DSS (v4.0 – 6.3.3): Demands prompt patching of known vulnerabilities.
More on PCI-DSS
Risk Identification
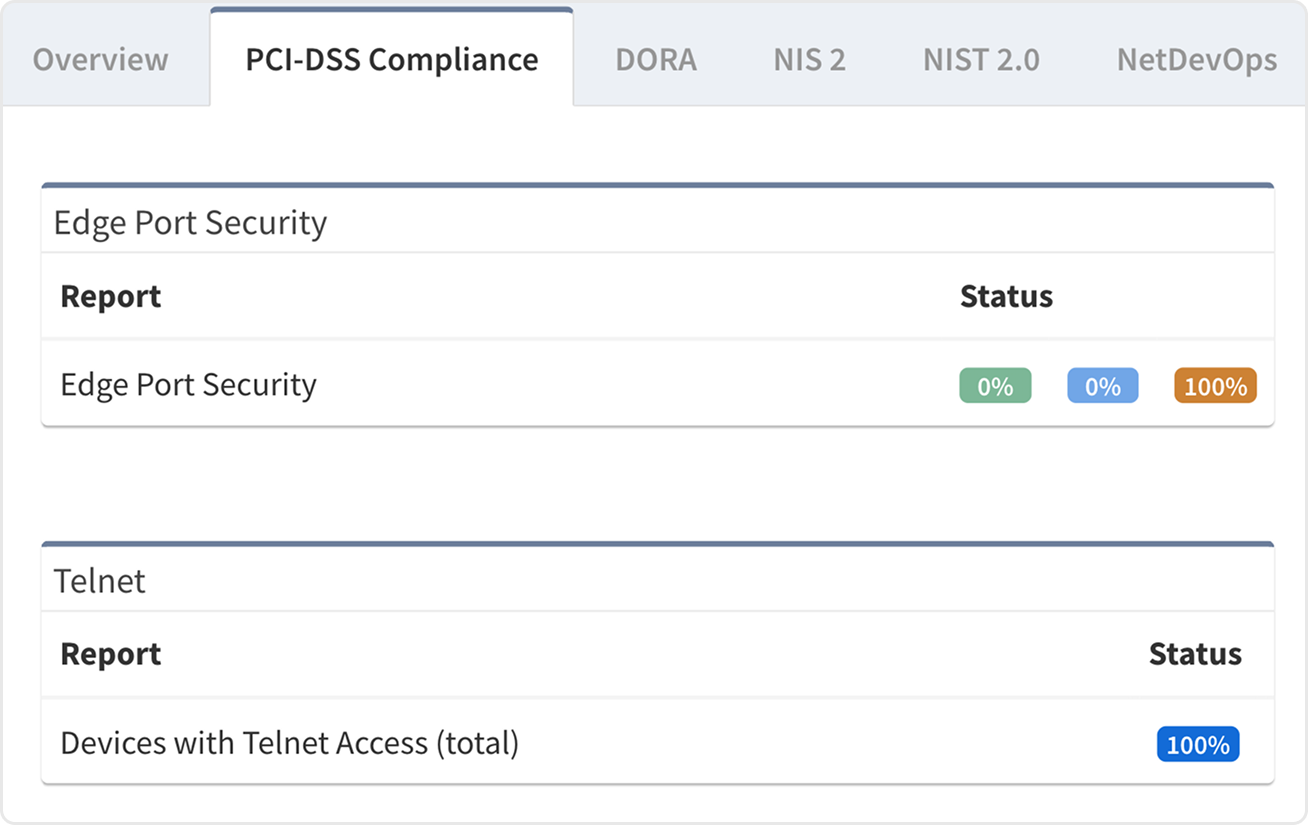
Network devices with Telnet access may represent a violation of PCI DSS (v4.0 – Requirement 2.2.6 & 8.2.2), which disallows use of insecure protocols unless justified and protected with compensating controls.
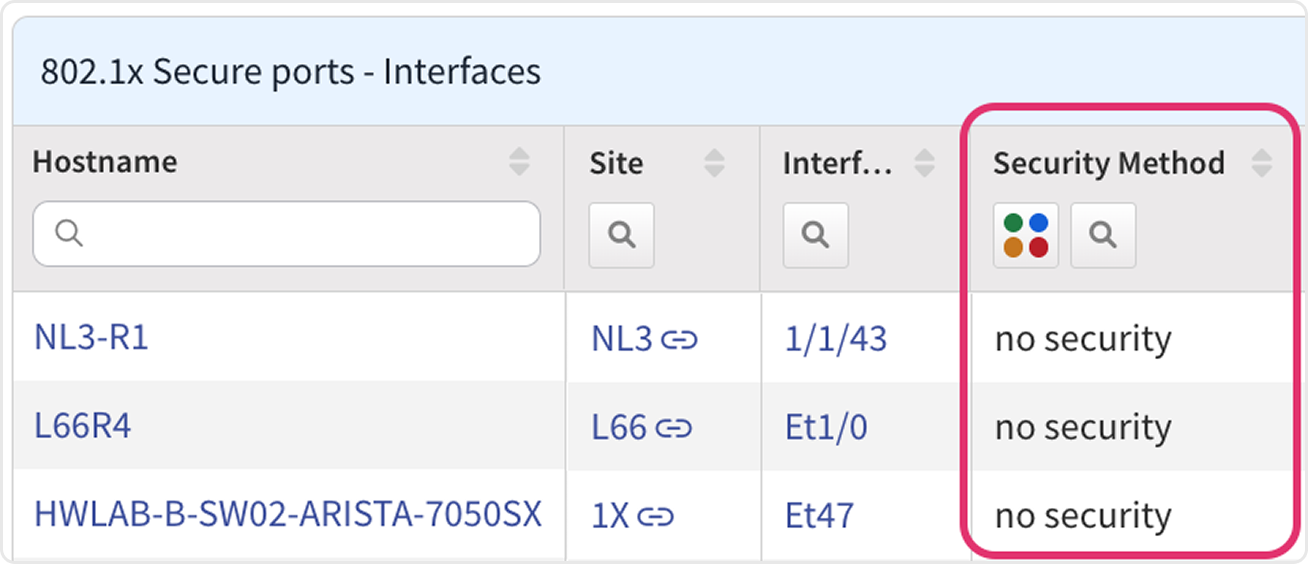
PCI DSS (v4.0 – Requirement 7 & 8): Mandates strong access controls and unique authentication for all users with access to cardholder data. 802.1X ensures only authenticated endpoints can reach scoped environments.
More on PCI-DSS
Configuration Backups
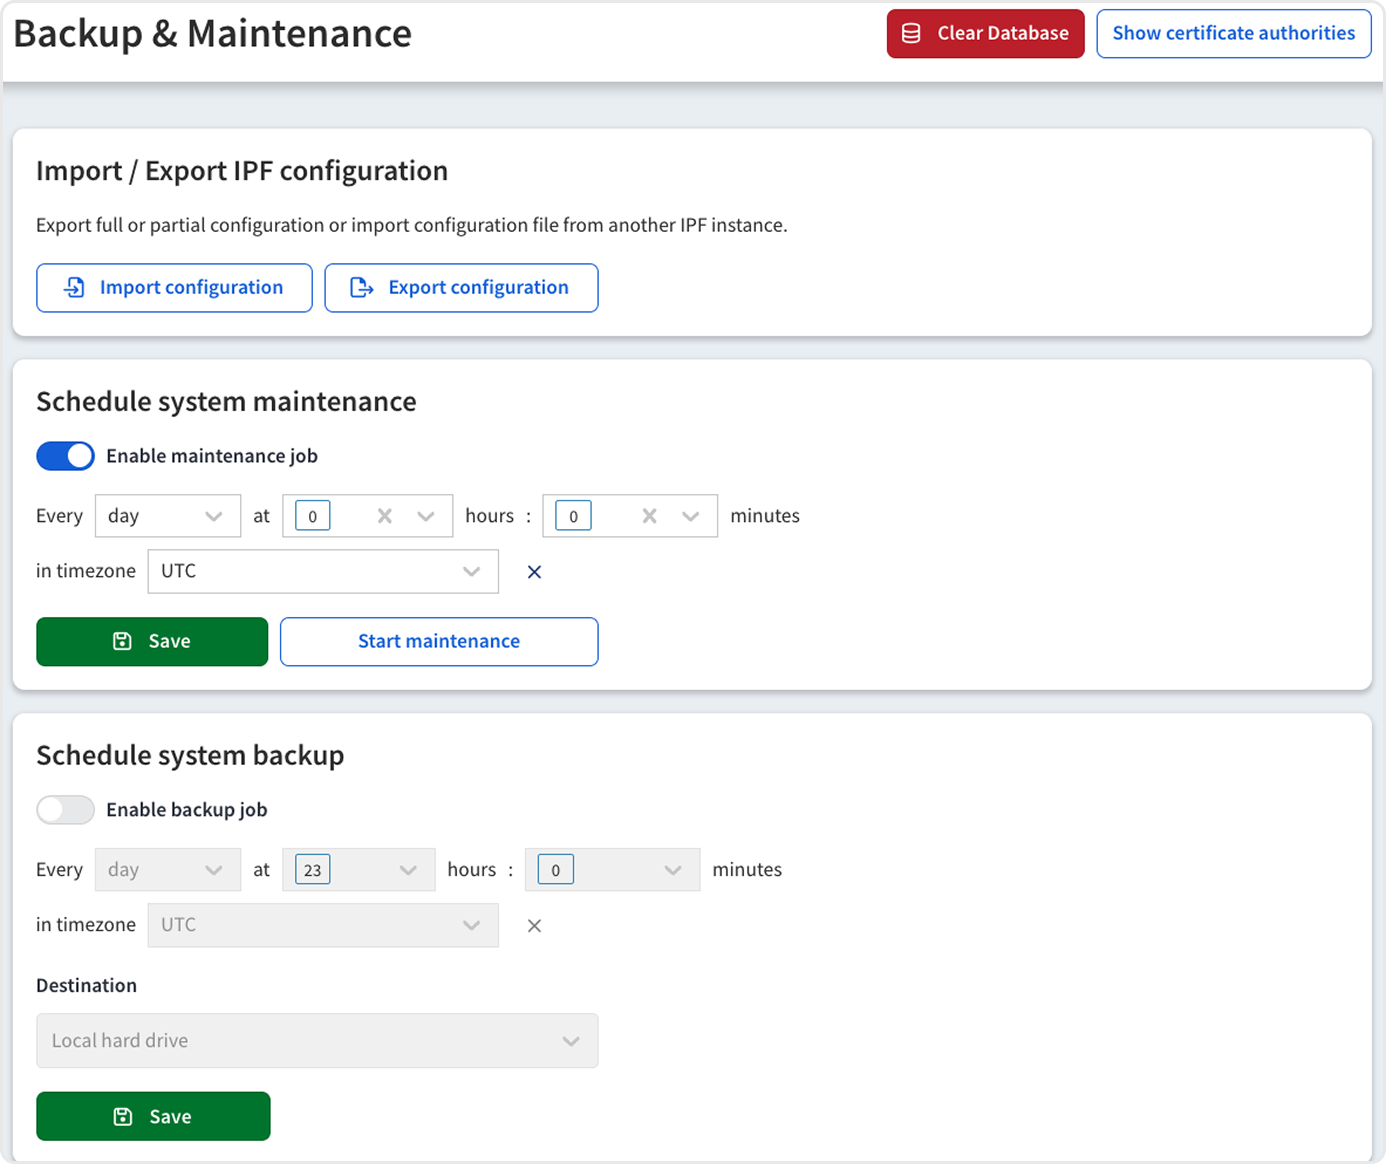
IP Fabric provides secure configuration backups to use in business continuity, network availability, and disaster recovery plans.
More on PCI-DSS
Security Policy Validation

Intent Check Confirming IPSec Tunnel Status
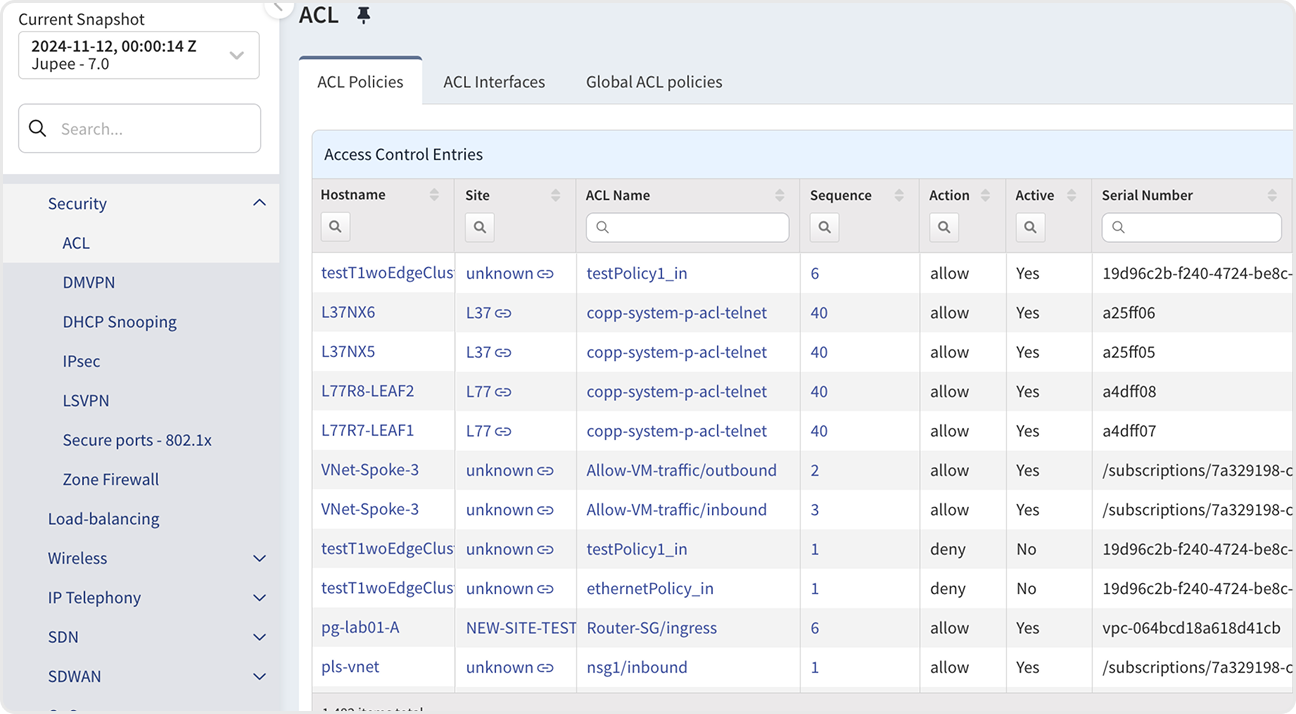
ACL Details
IP Fabric supplies key security information team that network teams need, giving a common language for network and security teams to understand the infrastructure through, ensuring proactivity, fast incident resolution (lower MTTR), and less friction between teams.
More on PCI-DSS
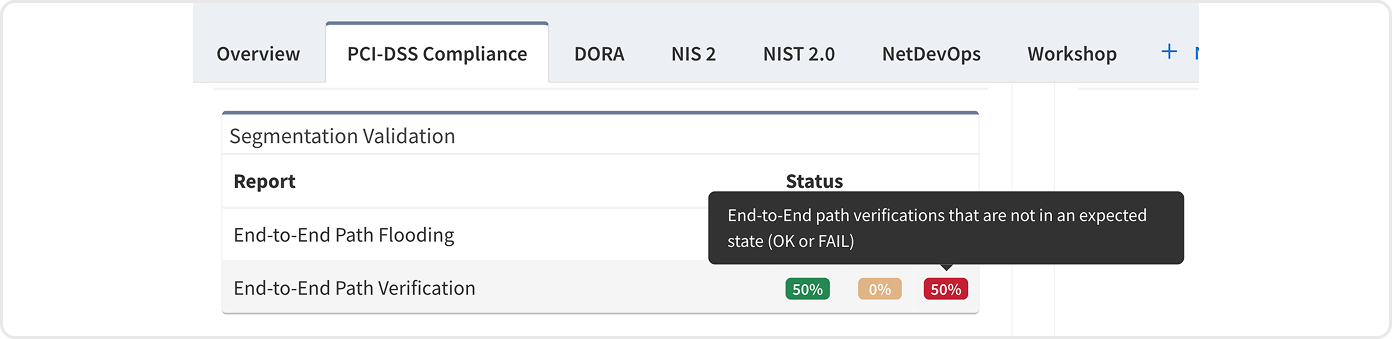
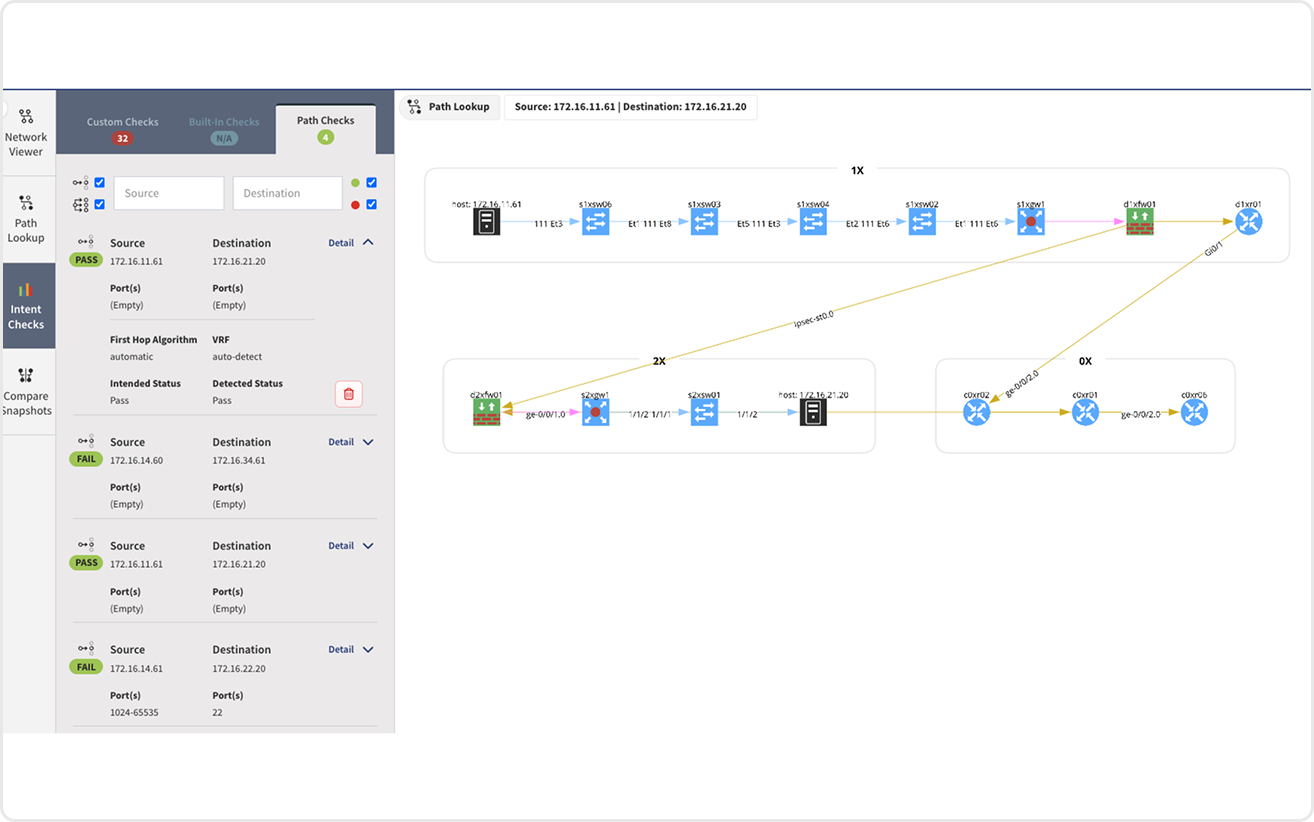
Segmentation Validation
More on PCI-DSS
End to End Analysis
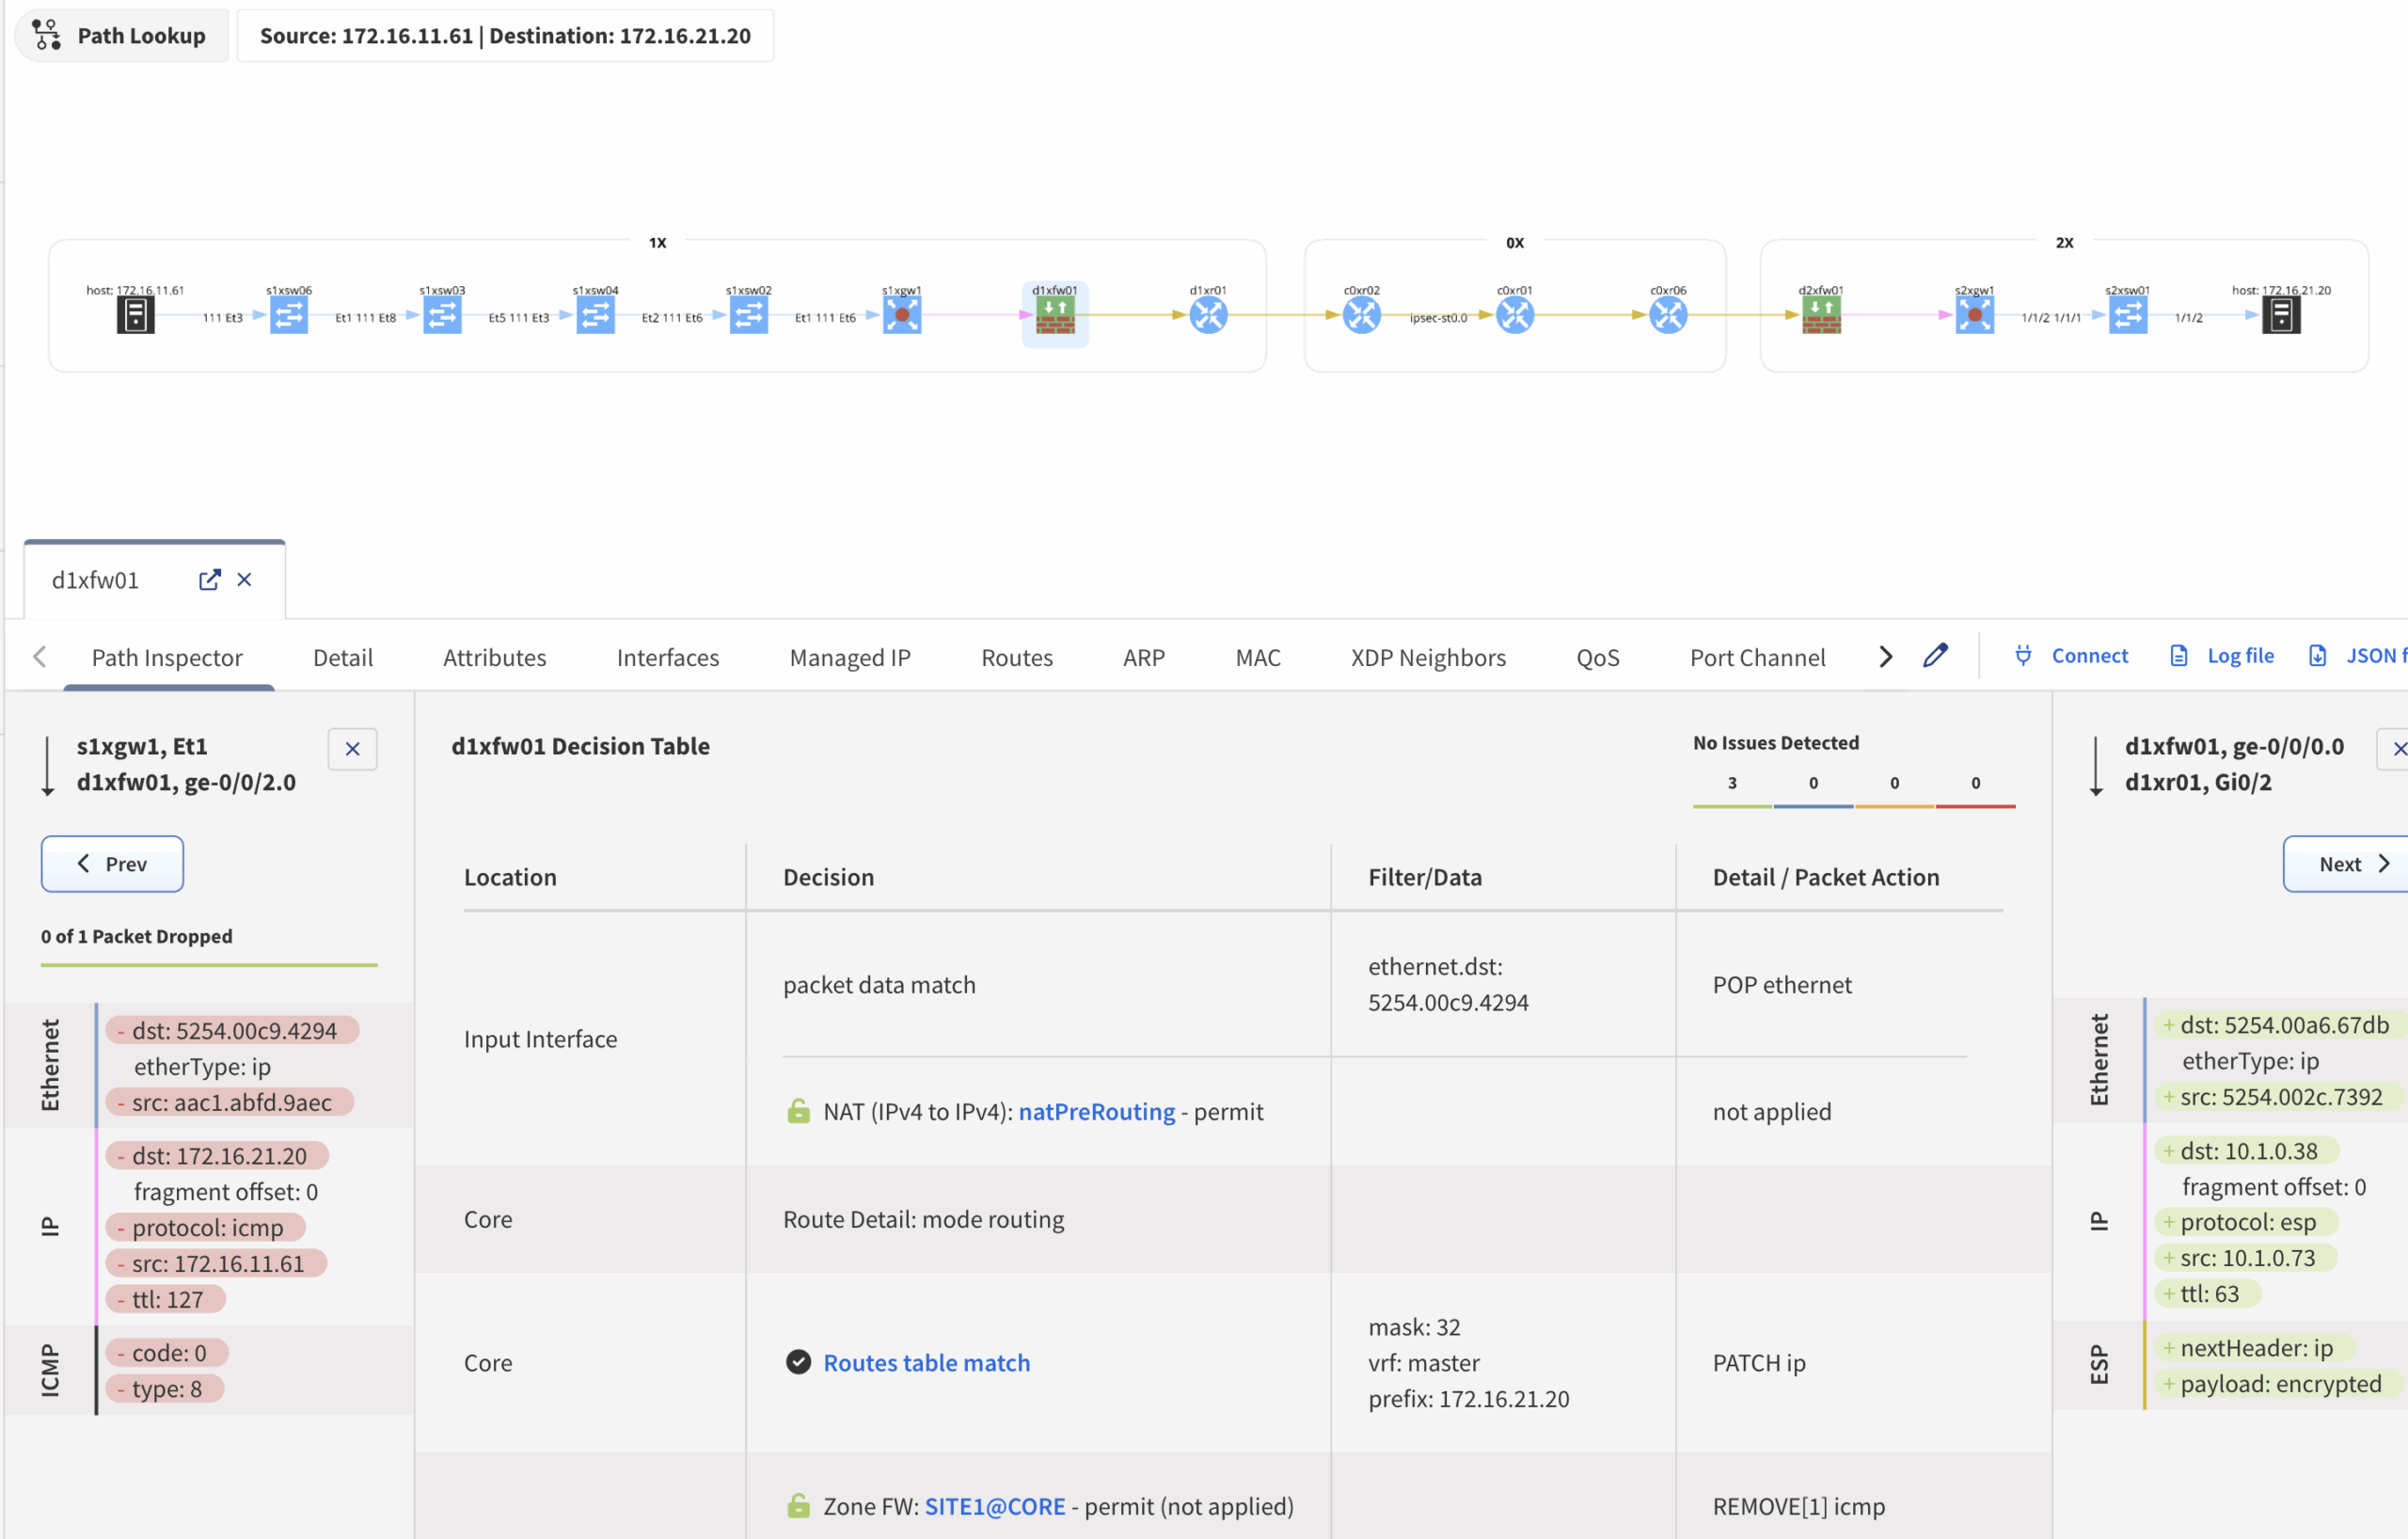
Automated End-to-End path visualization and analysis cuts out a repetitive manual data gathering process; saved path checks mean teams can quickly understand critical path status with every snapshot.
More on PCI-DSS
Business Continuity Validation
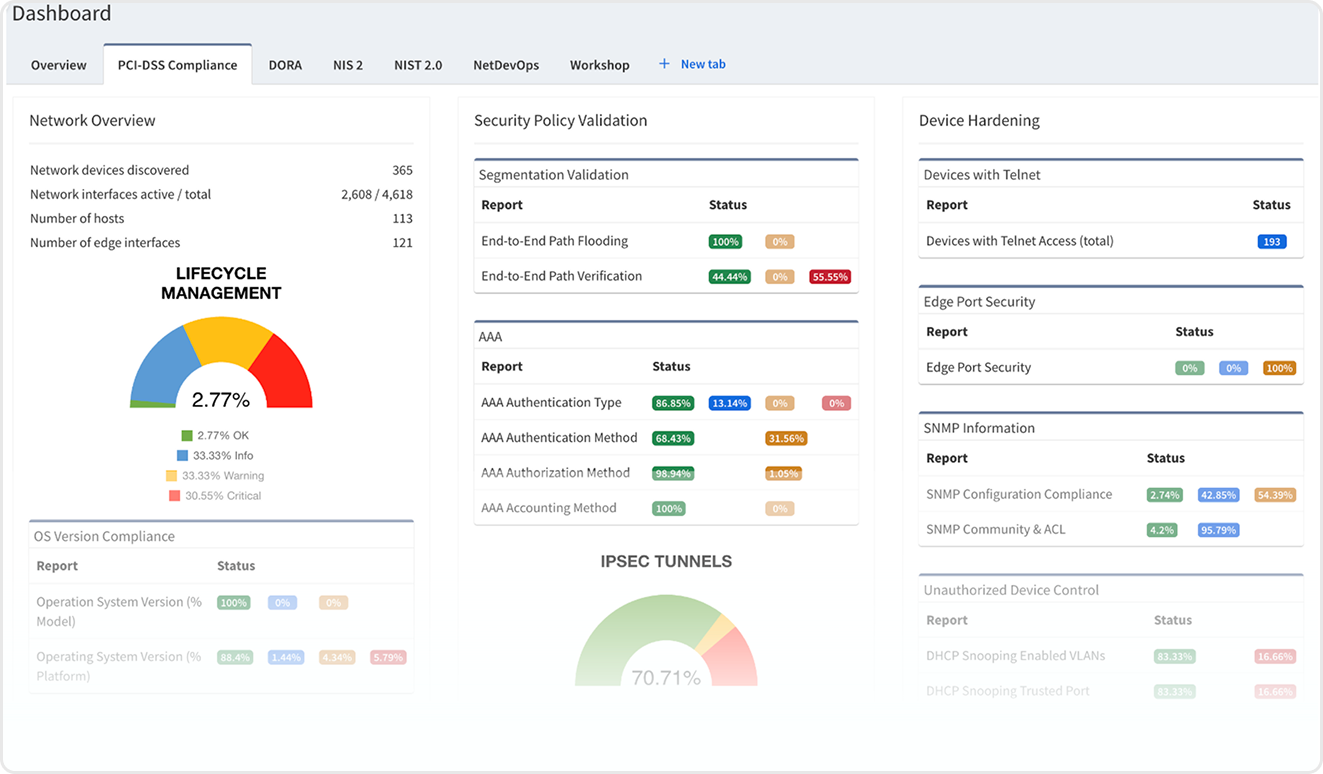
Custom Dashboards for specific critical network segments or teams allow for a daily overview of business continuity, that you can securely share with a specific audience.
More on PCI-DSS
Automated Incident Reponse
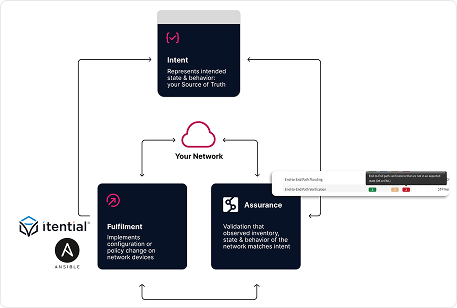
Use IP Fabric’s open REST API to trigger, and then validate, automated incident response.
More on PCI-DSS
Automated Custom Reports
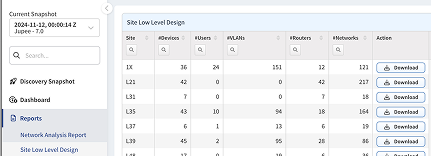
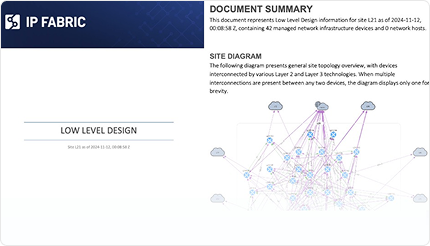
Most regulations give short windows for reporting on the state of the network; IP Fabric provides consumable reports with a click and the option to automate creation of custom network reports.
More on PCI-DSS
Daily Discovery & Inventory
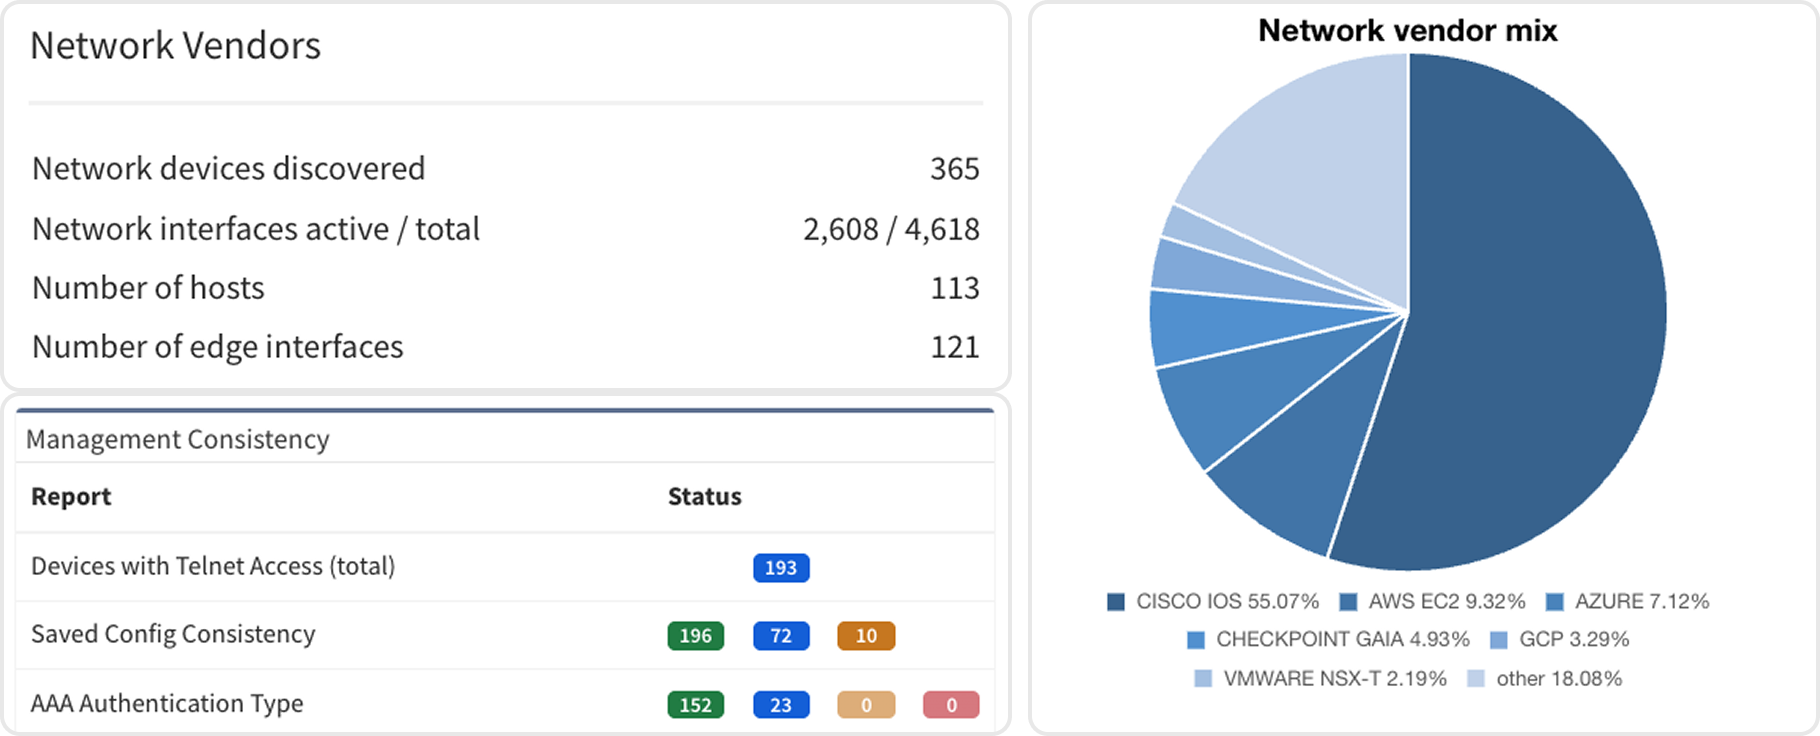
Network devices with Telnet access may represent a violation of PCI DSS (v4.0 – Requirement 2.2.6 & 8.2.2), which disallows use of insecure protocols unless justified and protected with compensating controls. Manually collecting and documenting this information is time-consuming and often inaccurate, leaving you subject to violations, and consequently, monetary and administrative penalties.
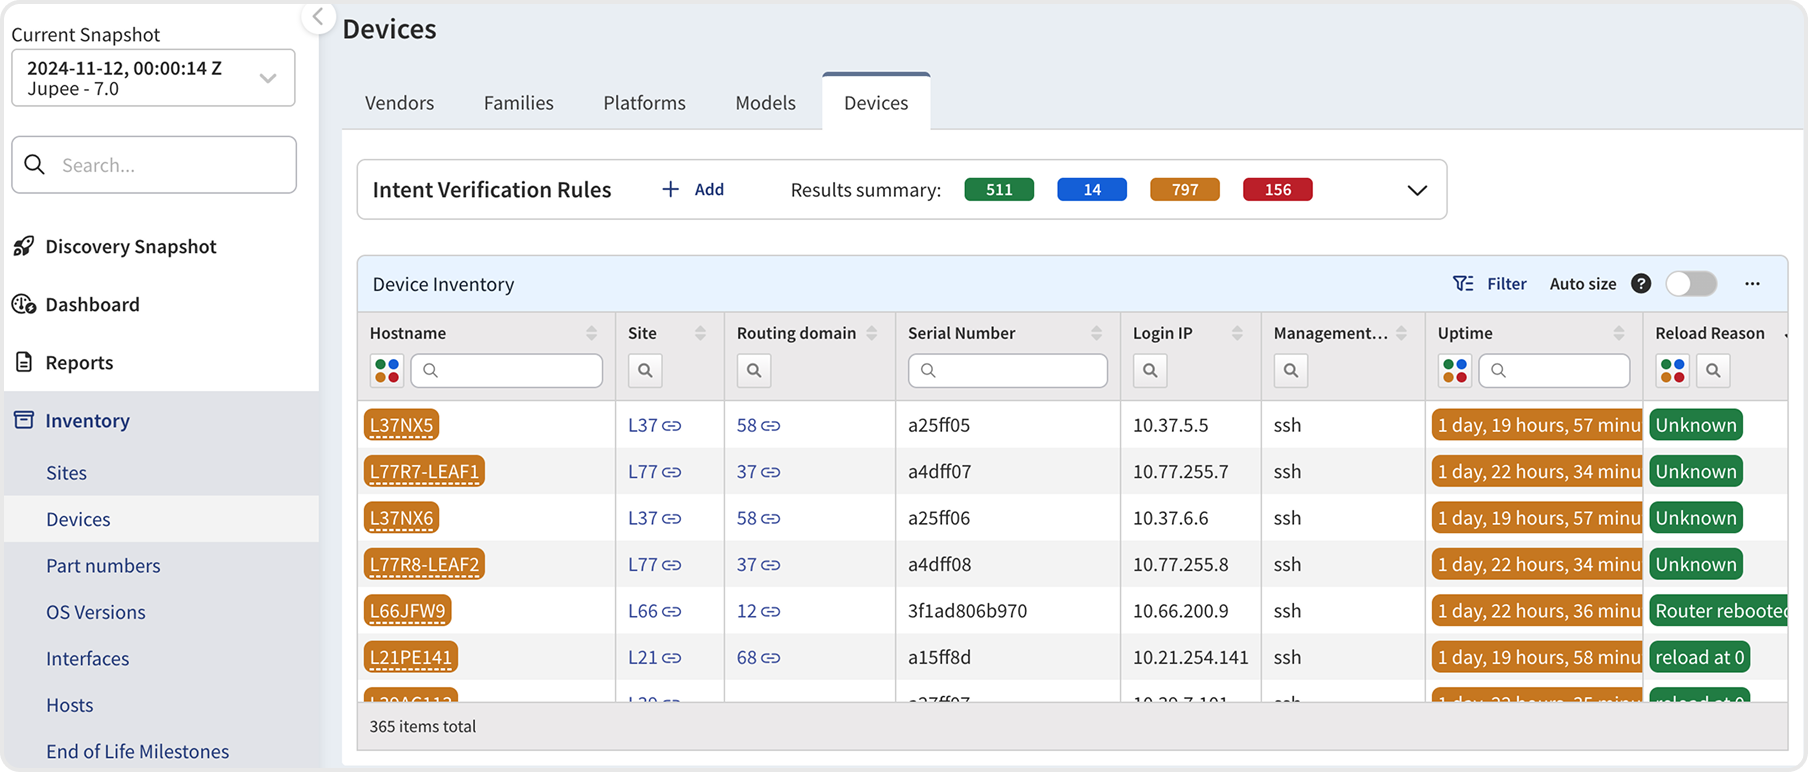
A fortified network device inventory represents the point-in-time “inventory of system” PCI requires.
More on DORA
Lifecycle Management
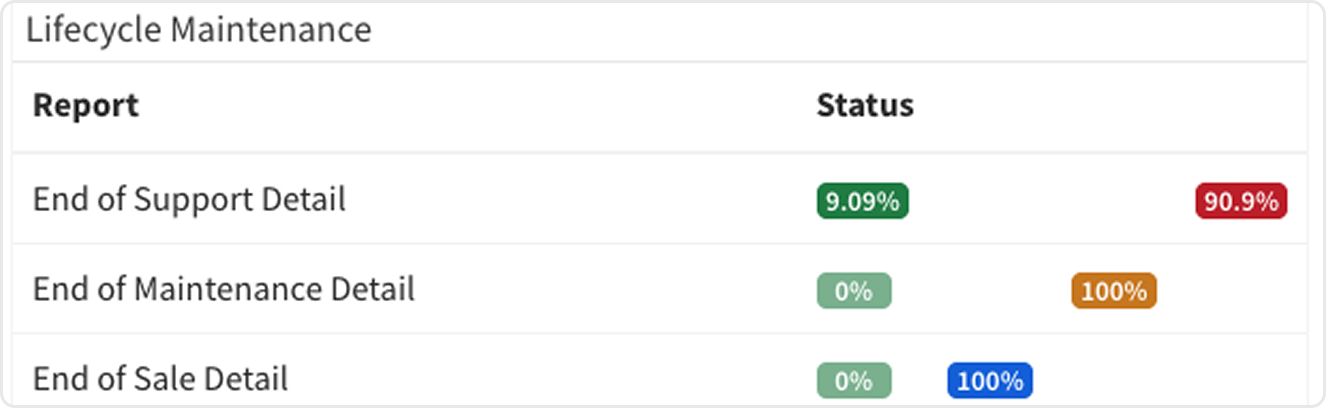
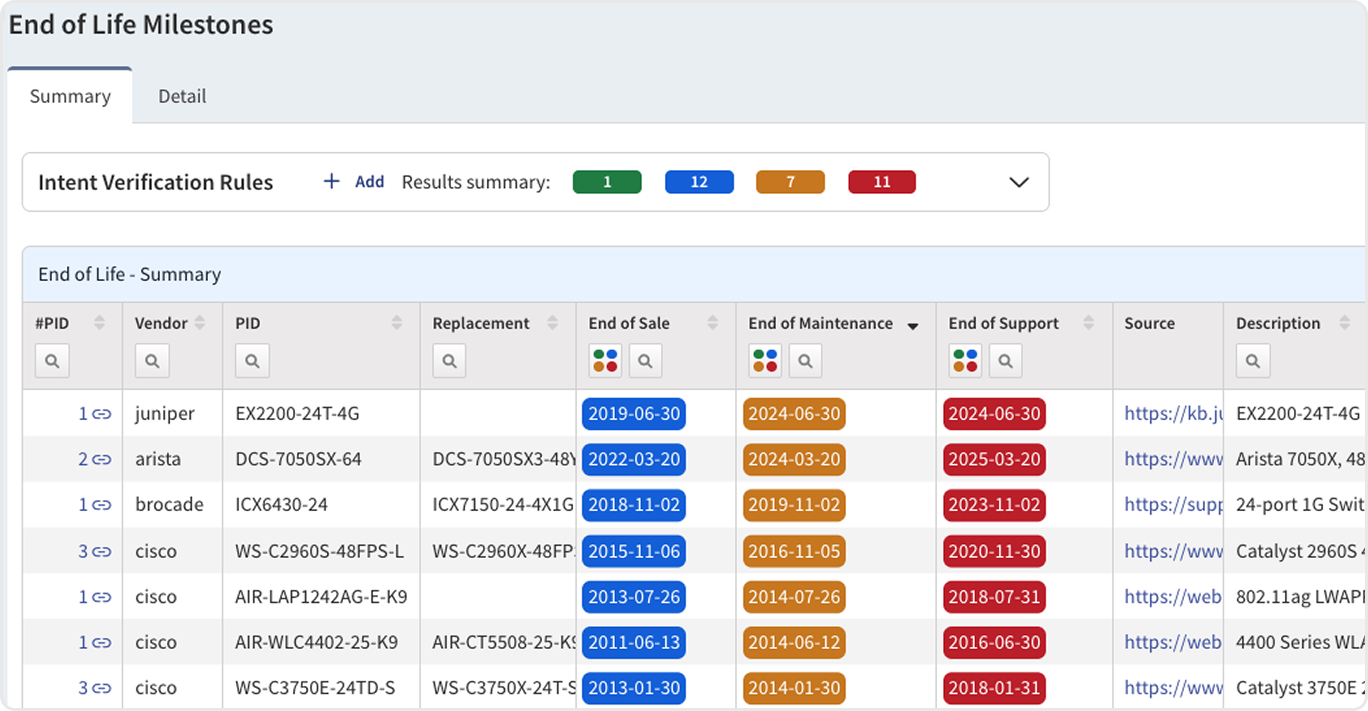
IP Fabric provides detailed Lifecycle Maintenance Information with every snapshot – automating collection and normalization of this data from disparate vendors and technologies ensures accurate planning, reporting, and operation of critical networks.
Devices that have reached end-of-life (EOL), end-of-maintenance, or end-of-support may no longer receive critical security updates, firmware patches, or vendor assistance, making them vulnerable to exploitation and non-compliant with most security standards.DORA expects systems to be “state-of-the-art” and regularly assessed for risk — outdated systems breach this expectation.
More on DORA
Risk Identification
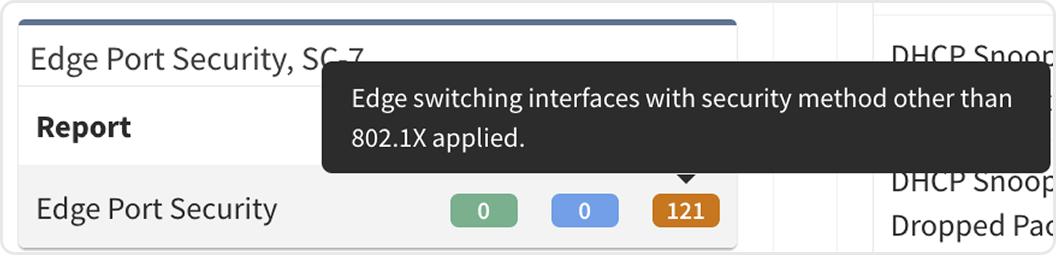
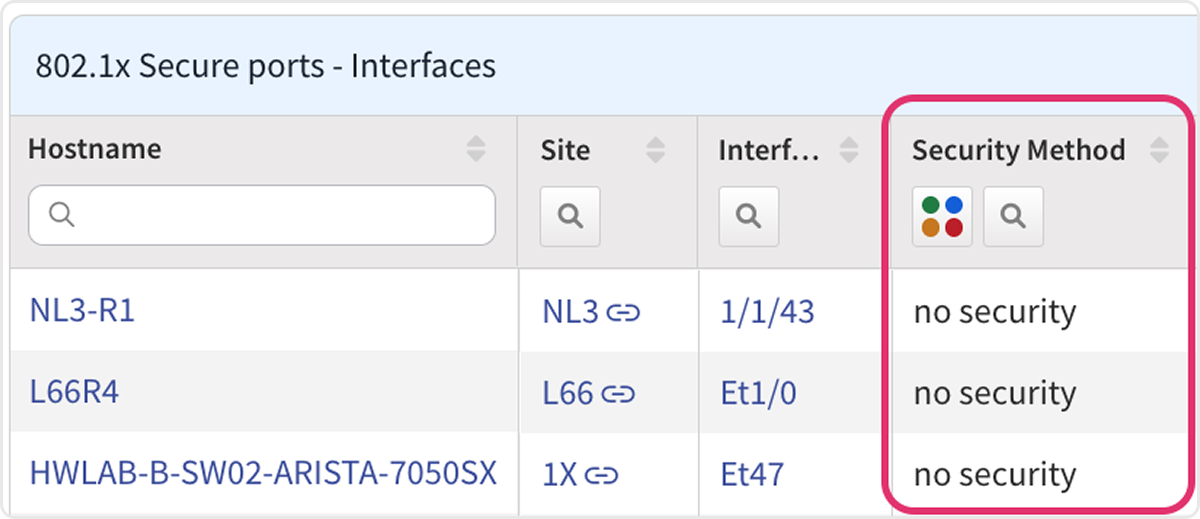
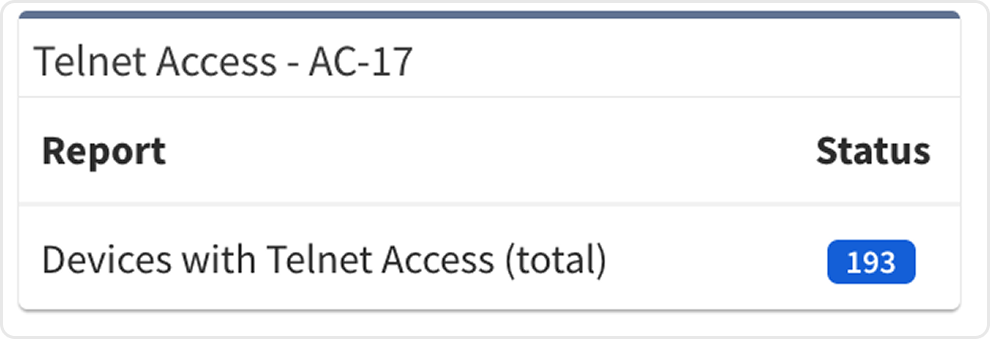
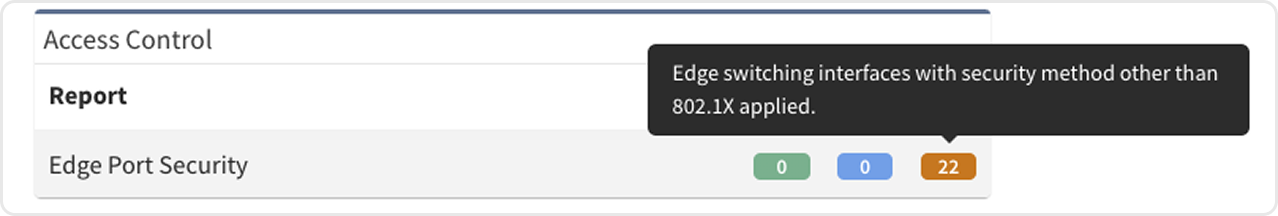
DORA calls for robust ICT risk management, including identity and access management (IAM). 802.1X enforces hardware-based IAM at the physical and logical network layers.
More on DORA
Configuration Backups
IP Fabric provides secure configuration backups to use in business continuity, network availability, and disaster recovery plans.
More on DORA
Security Policy Validation
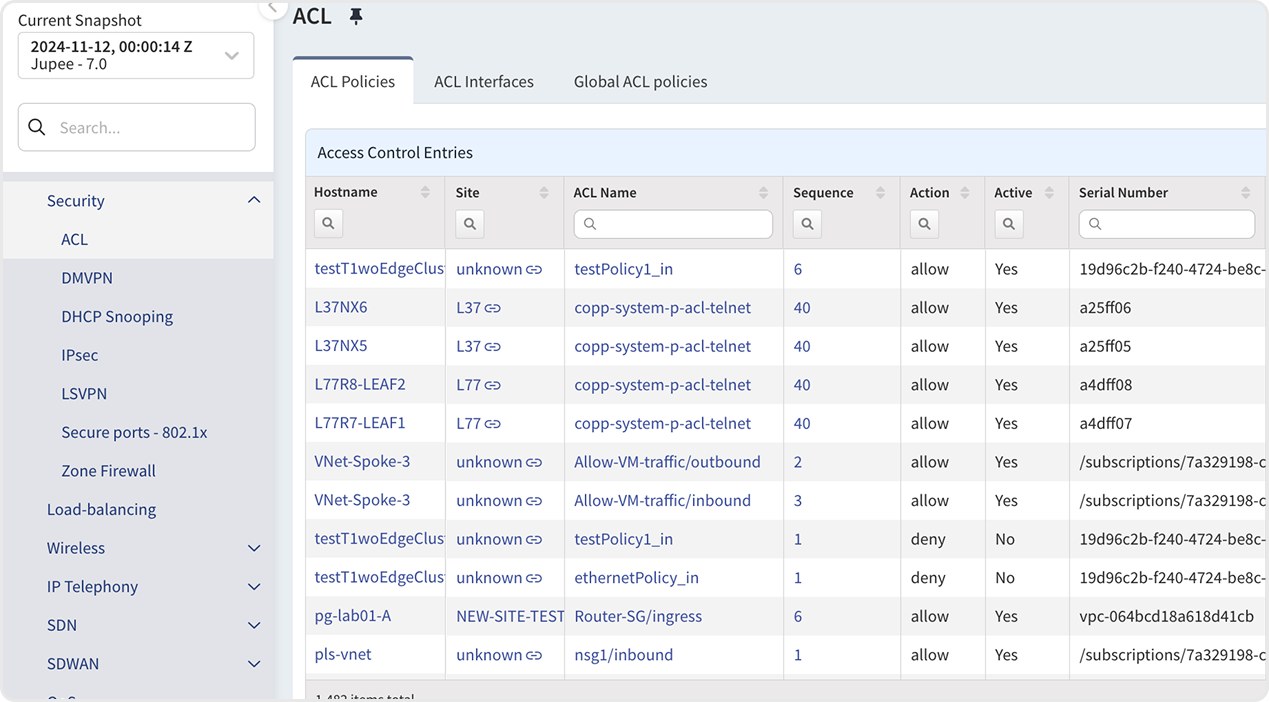
IP Fabric supplies key security information team that network teams need, giving a common language for network and security teams to understand the infrastructure through, ensuring proactivity, fast incident resolution (lower MTTR), and less friction between teams.
More on DORA
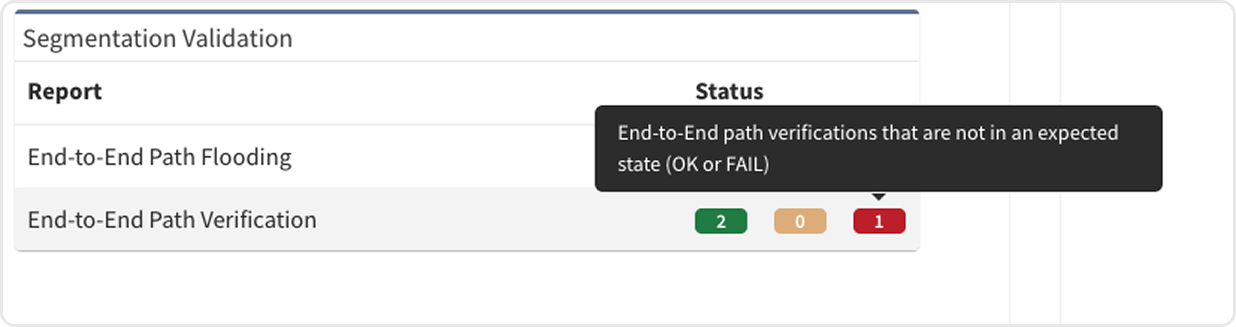
Segmentation Validation
More on DORA
End to End Analysis
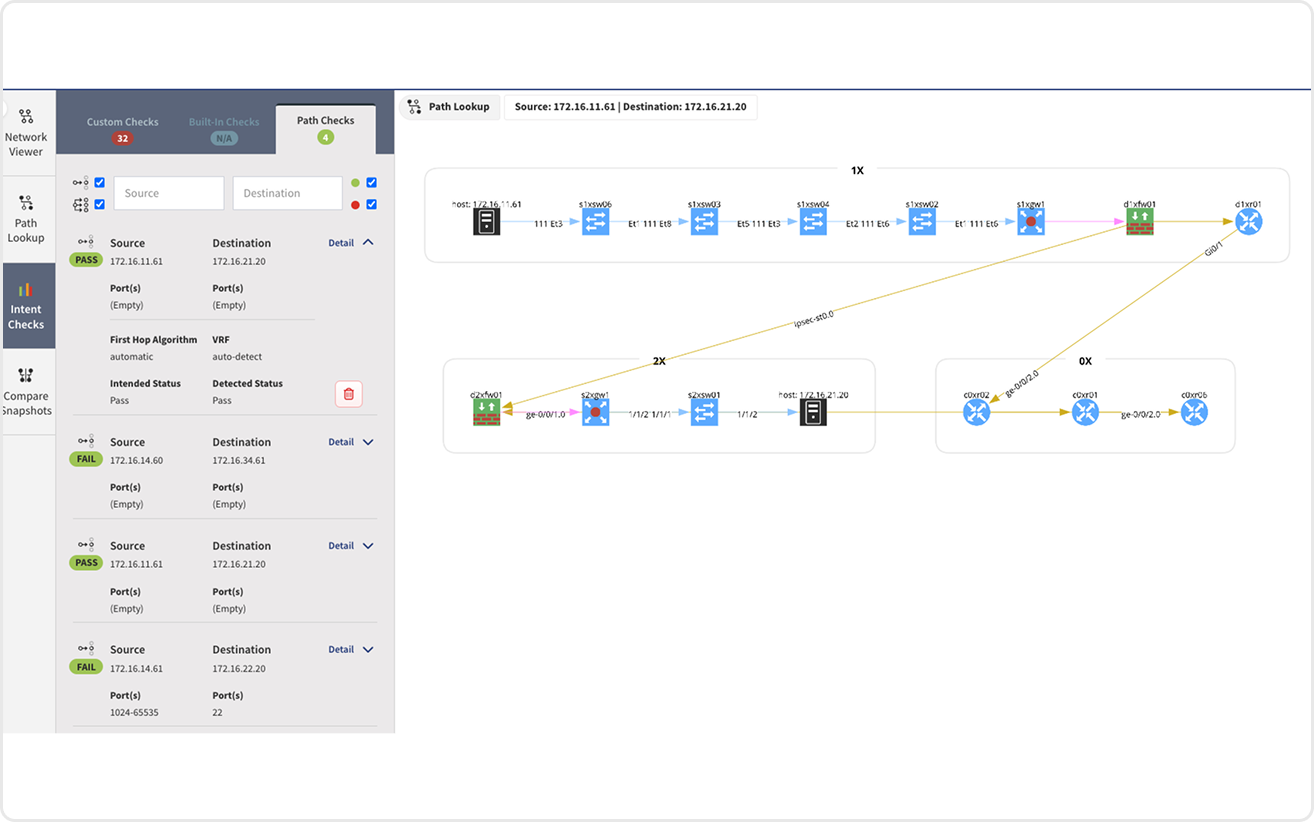
Automated End-to-End path visualization and analysis cuts out a repetitive manual data gathering process; saved path checks mean teams can quickly understand critical path status with every snapshot.
More on DORA
Business Continuity Validation
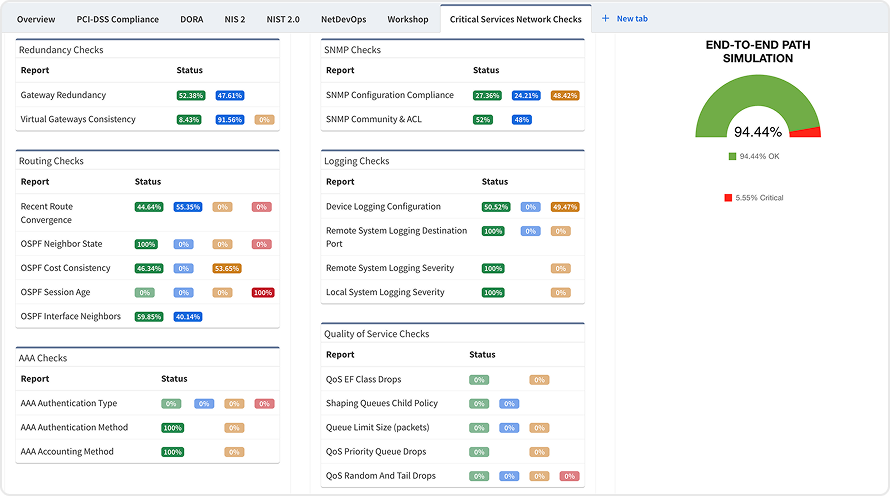
Custom Dashboards for specific critical network segments or teams allow for a daily overview of business continuity, that you can securely share with a specific audience.
More on DORA
Automated Incident Reponse
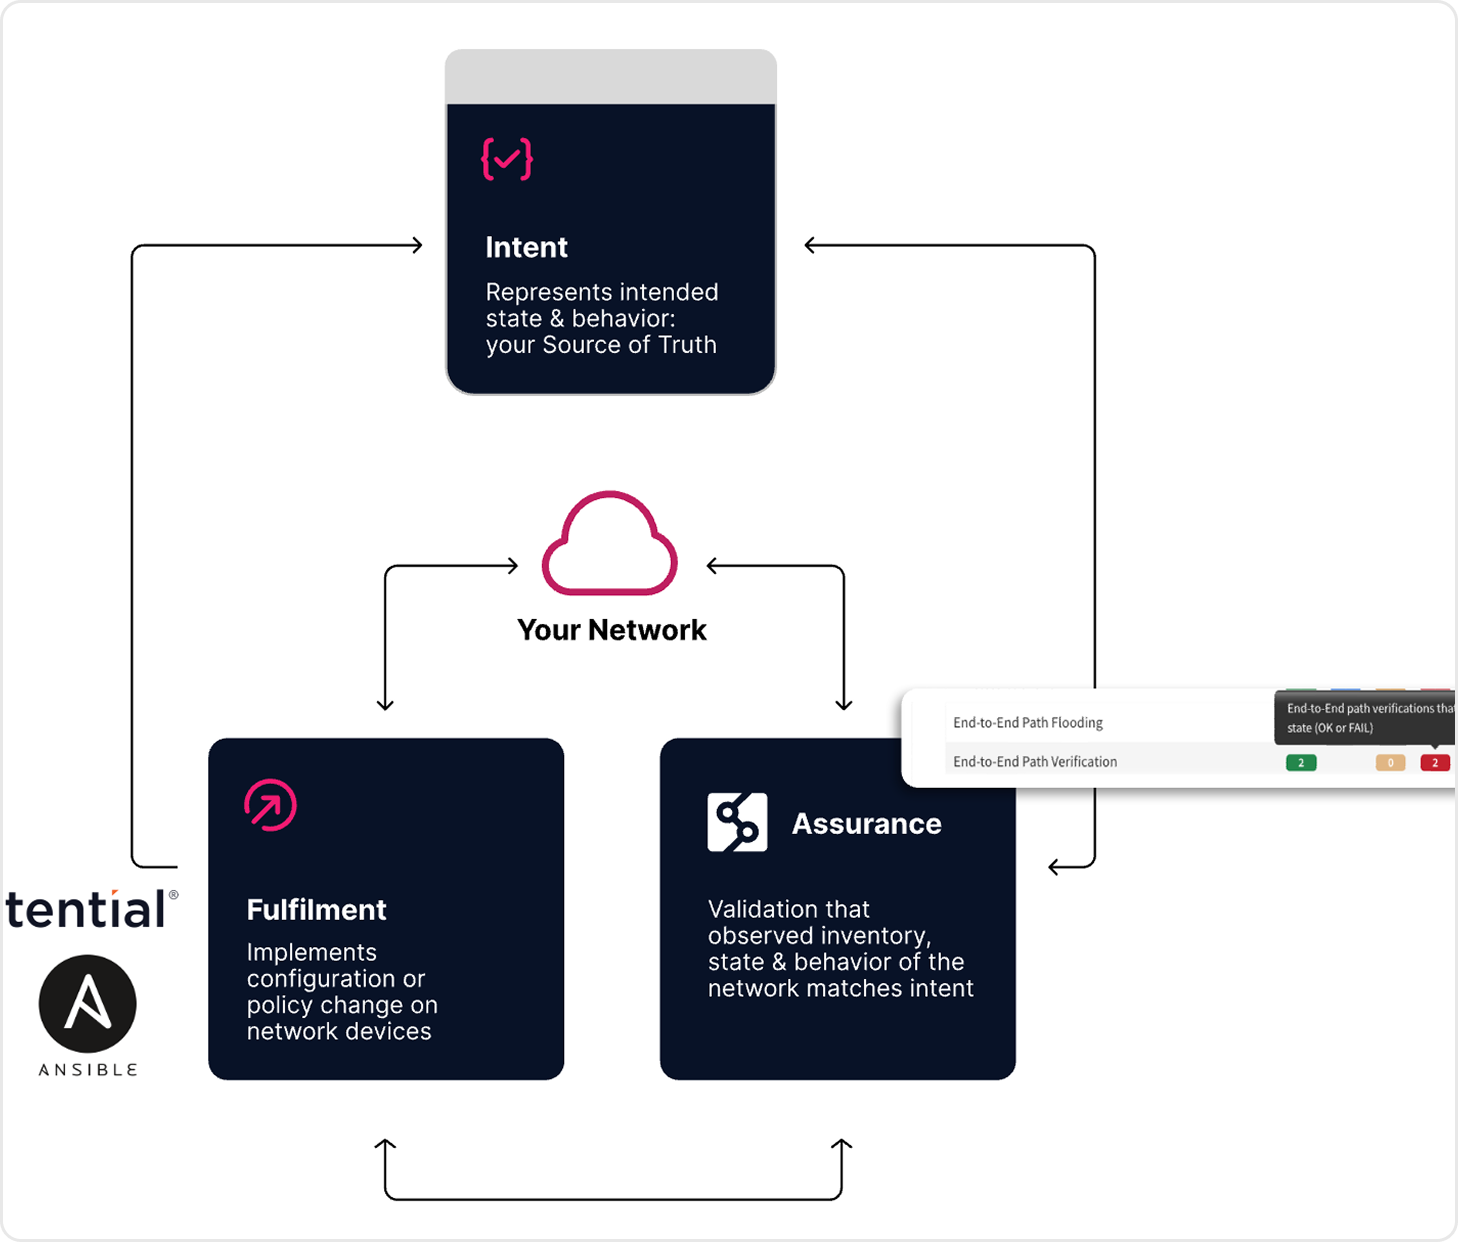
Use IP Fabric’s open REST API to trigger, and then validate, automated incident response.
More on DORA
Automated Custom Reports
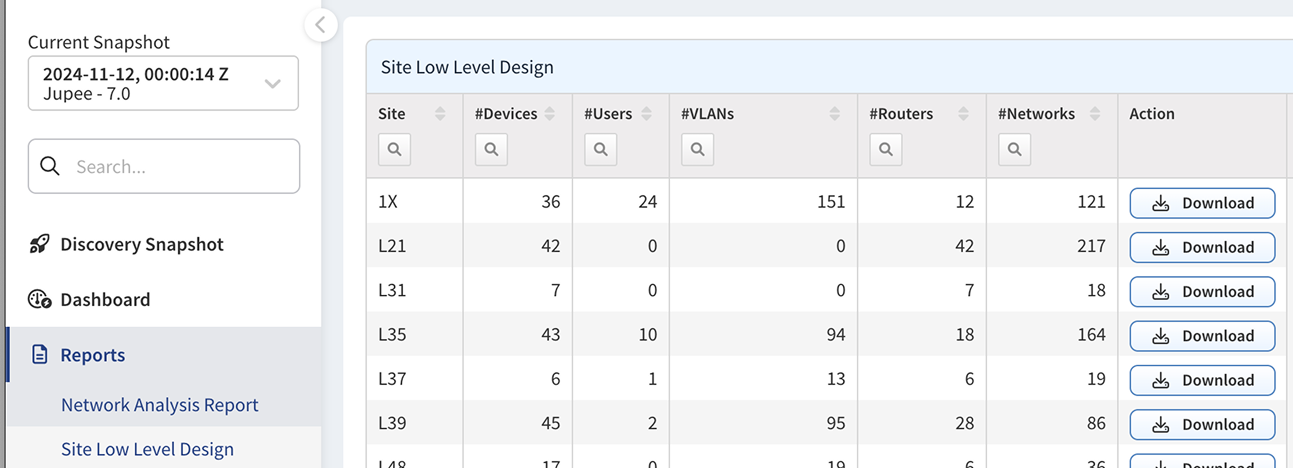
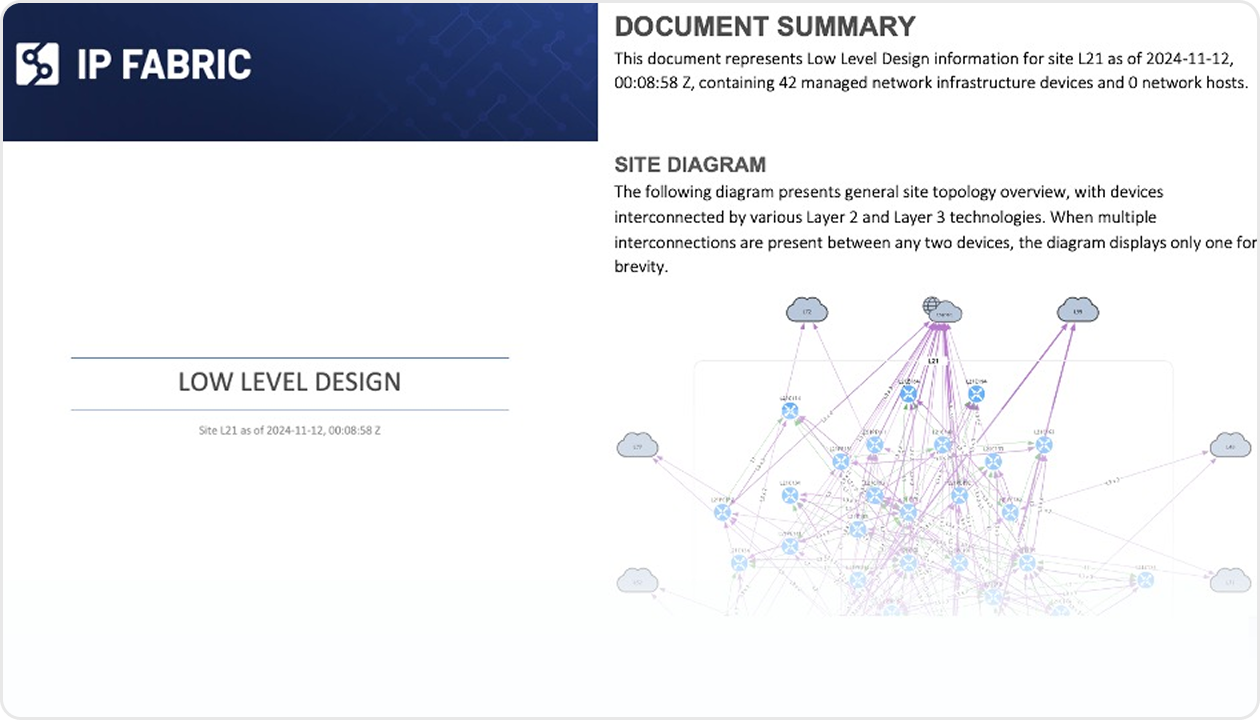
Most regulations give short windows for reporting on the state of the network; IP Fabric provides consumable reports with a click and the option to automate creation of custom network reports.
More on DORA
Daily Discovery & Inventory
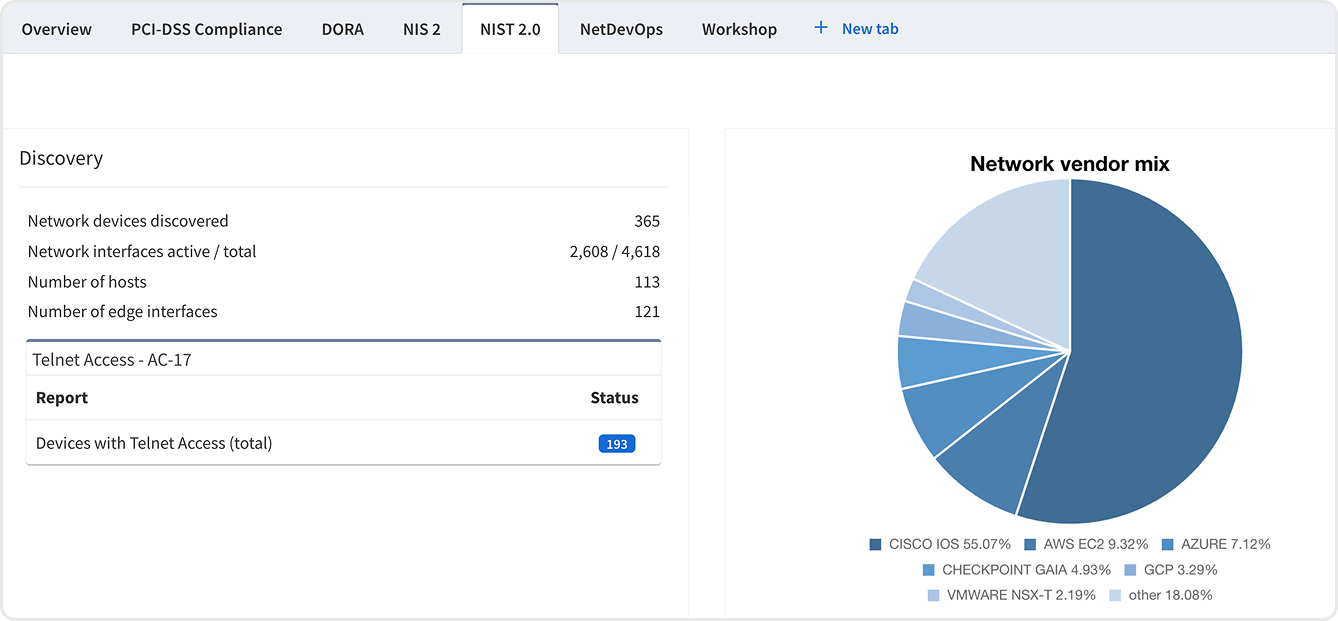
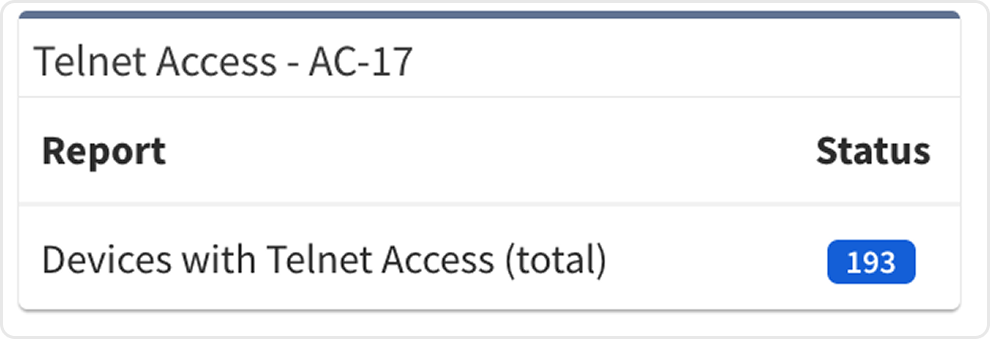
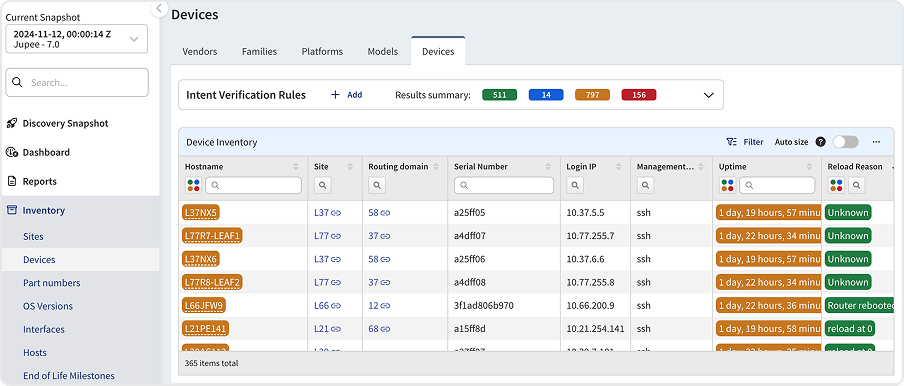
Network devices with Telnet access may represent a violation of NIST (e.g., SP 800-53, CSF): Requires use of secure protocols like SSH for remote device management. Telnet would be flagged under controls related to access control (AC-17) and system communication protection (SC-12). Manually collecting and documenting this information is time-consuming and often inaccurate, leaving you subject to violations, and consequently, monetary and administrative penalties.
A fortified network device inventory represents the point-in-time “inventory of assets” and “baseline configuration of systems” NIST requires.
More on NIST
Lifecycle Management
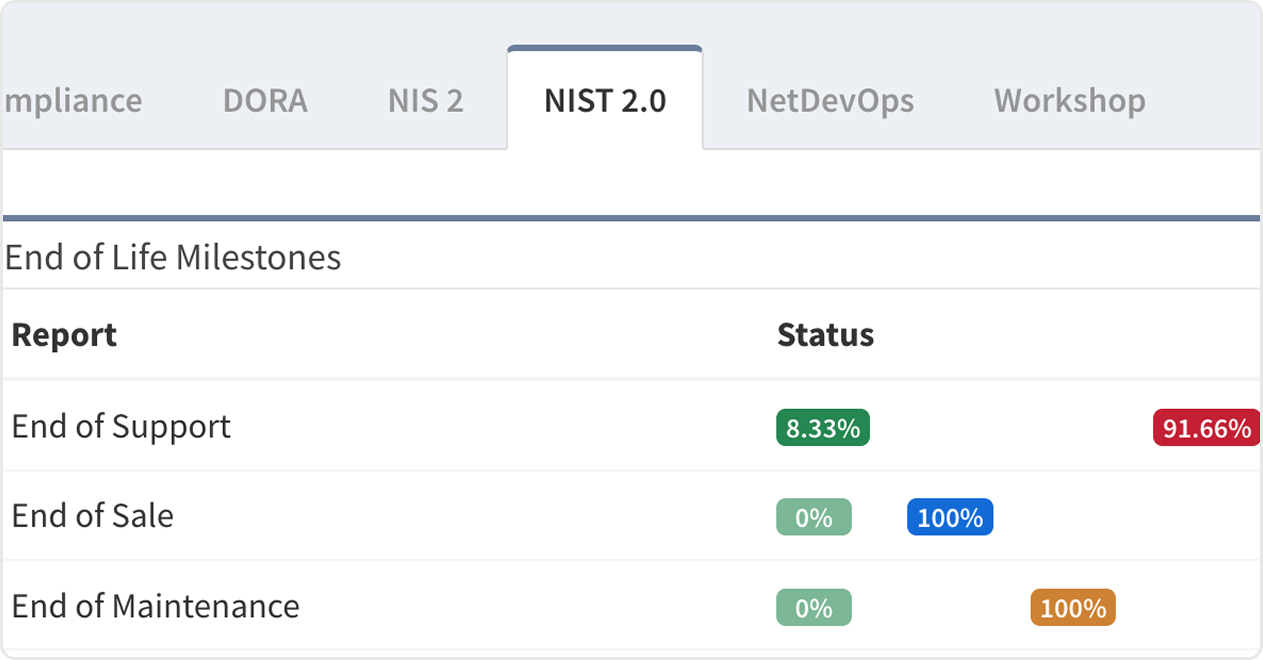
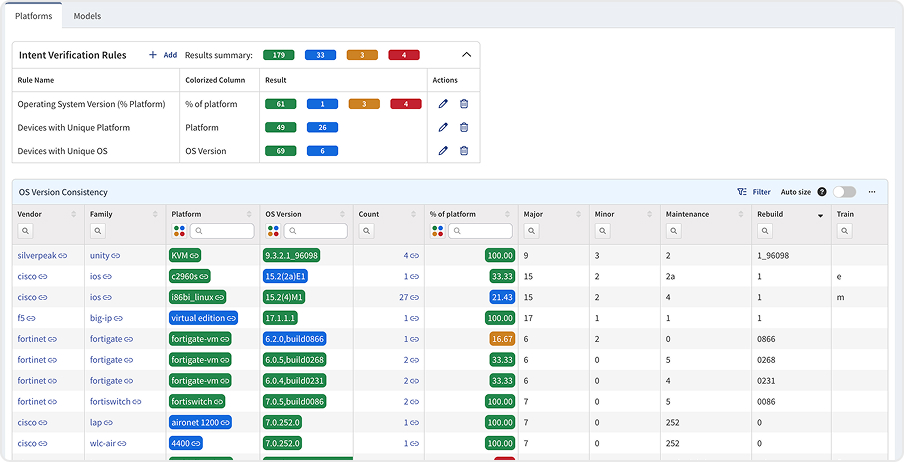
Devices that have reached end-of-life (EOL), end-of-maintenance, or end-of-support may no longer receive critical security updates, firmware patches, or vendor assistance, making them vulnerable to exploitation and non-compliant with most security standards. NIST (CM-2, SI-2, RA-5): Requires timely vulnerability remediation and lifecycle awareness.
More on NIST
Risk Identification
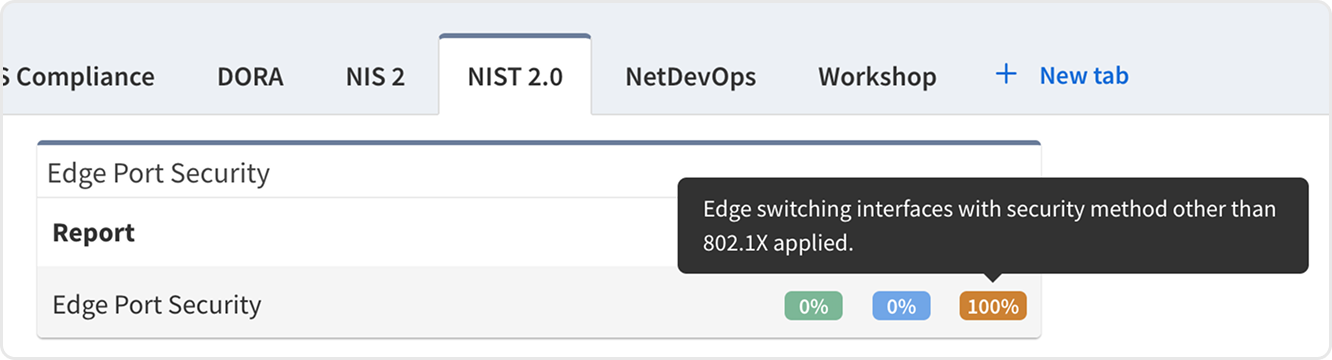
Security frameworks require enforcement of network access control and multi-factor authentication where applicable. 802.1X supports identity-based network segmentation and endpoint validation, aligning with Zero Trust principles.
More on NIST
Configuration Backups
IP Fabric provides secure configuration backups to use in business continuity, network availability, and disaster recovery plans.
More on NIST
Security Policy Validation
IP Fabric supplies key security information team that network teams need, giving a common language for network and security teams to understand the infrastructure through, ensuring proactivity, fast incident resolution (lower MTTR), and less friction between teams.
More on NIST
Segmentation Validation
More on NIST
End to End Analysis
Automated End-to-End path visualization and analysis cuts out a repetitive manual data gathering process; saved path checks mean teams can quickly understand critical path status with every snapshot.
More on NIST
Business Continuity Validation
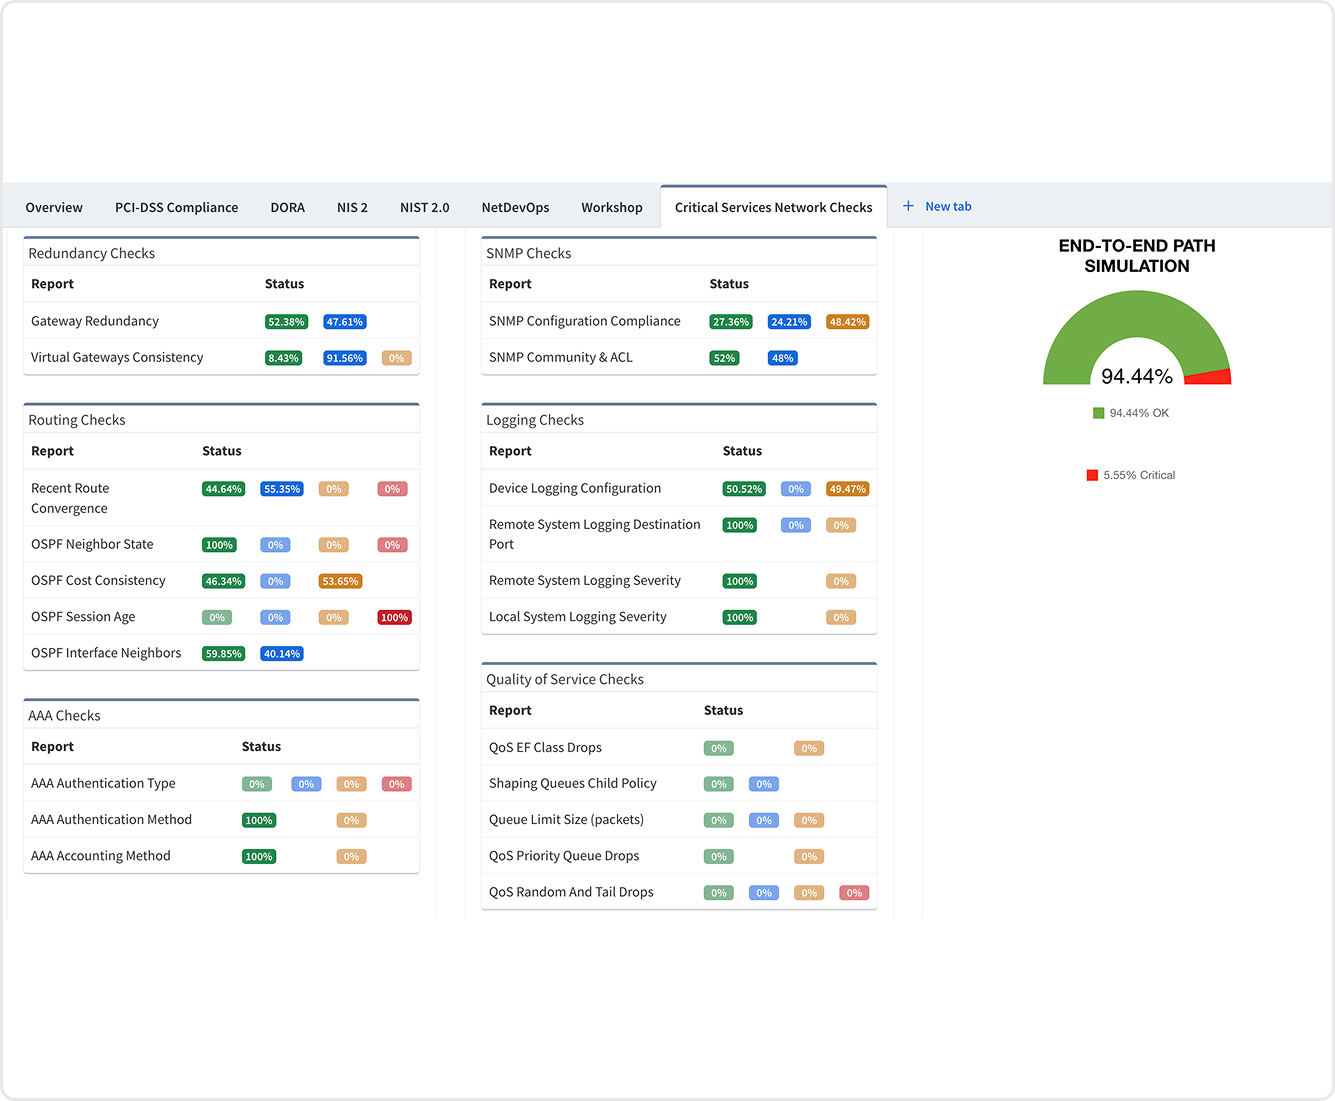
More on NIST
Automated Incident Reponse
Use IP Fabric’s open REST API to trigger, and then validate, automated incident response.
More on NIST
Automated Custom Reports
Most regulations give short windows for reporting on the state of the network; IP Fabric provides consumable reports with a click and the option to automate creation of custom network reports.
More on NIST
Daily Discovery & Inventory
More on NIS 2
Lifecycle Management
IP Fabric provides detailed Lifecycle Maintenance Information with every snapshot – automating collection and normalization of this data from disparate vendors and technologies ensures accurate planning, reporting, and operation of critical networks.
More on NIS 2
Risk Identification
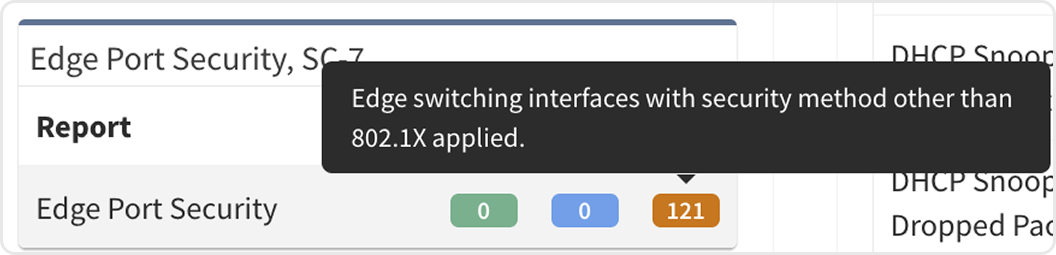
NIS2 (Article 21): Requires access control policies and protection of network and information systems. 802.1X supports risk-based access enforcement and reduces exposure to unauthorized devices.
More on NIS 2
Configuration Backups
IP Fabric provides secure configuration backups to use in business continuity, network availability, and disaster recovery plans.
More on NIS 2
Security Policy Validation
IP Fabric supplies key security information team that network teams need, giving a common language for network and security teams to understand the infrastructure through, ensuring proactivity, fast incident resolution (lower MTTR), and less friction between teams.
More on NIS 2
Segmentation Validation
More on NIS 2
End to End Analysis
Automated End-to-End path visualization and analysis cuts out a repetitive manual data gathering process; saved path checks mean teams can quickly understand critical path status with every snapshot.
More on NIS 2
Business Continuity Validation
More on NIS 2
Automated Incident Reponse
Use IP Fabric’s open REST API to trigger, and then validate, automated incident response.
More on NIS 2
Automated Custom Reports
Most regulations give short windows for reporting on the state of the network; IP Fabric provides consumable reports with a click and the option to automate creation of custom network reports.
More on NIS 2
Daily Discovery & Inventory
Network devices with Telnet Access may represent a violation of HIPAA (45 CFR §164.312(e)): Requires protection of data in transit, which Telnet fails to provide.
Manually collecting and documenting this information is time-consuming and often inaccurate, leaving you subject to violations, and consequently, monetary and administrative penalties.
A fortified network device inventory ensures identification of all systems that access ePHI as specified by HIPAA. Failure to produce relevant inventories may result in tens of thousands in fines.
More on HIPAA
Lifecycle Management
IP Fabric provides detailed Lifecycle Maintenance Information with every snapshot – automating collection and normalization of this data from disparate vendors and technologies ensures accurate planning, reporting, and operation of critical networks.
More on HIPAA
Risk Identification
HIPAA (45 CFR §164.312(a)(1)): Requires technical access controls to allow only authorized access to ePHI. 802.1X helps enforce user and device authentication at the network edge.
HIPAA (45 CFR §164.312(e)): Requires protection of data in transit, which Telnet fails to provide.
More on HIPAA
Configuration Backups
IP Fabric provides secure configuration backups to use in business continuity, network availability, and disaster recovery plans.
More on HIPAA
Security Policy Validation
IP Fabric supplies key security information team that network teams need, giving a common language for network and security teams to understand the infrastructure through, ensuring proactivity, fast incident resolution (lower MTTR), and less friction between teams.
More on HIPAA
Segmentation Validation
More on HIPAA
End to End Analysis
Automated End-to-End path visualization and analysis cuts out a repetitive manual data gathering process; saved path checks mean teams can quickly understand critical path status with every snapshot.
More on HIPAA
Business Continuity Validation
Custom Dashboards for specific critical network segments or teams allow for a daily overview of business continuity, that you can securely share with a specific audience.
More on HIPAA
Automated Incident Reponse
Use IP Fabric’s open REST API to trigger, and then validate, automated incident response.
More on HIPAA
Automated Custom Reports
Most regulations give short windows for reporting on the state of the network; IP Fabric provides consumable reports with a click and the option to automate creation of custom network reports.
More on HIPAA
Daily Discovery & Inventory
More on ISO 27001
Lifecycle Management
IP Fabric provides detailed Lifecycle Maintenance Information with every snapshot – automating collection and normalization of this data from disparate vendors and technologies ensures accurate planning, reporting, and operation of critical networks.
More on ISO 27001
Risk Identification
More on ISO 27001
Configuration Backups
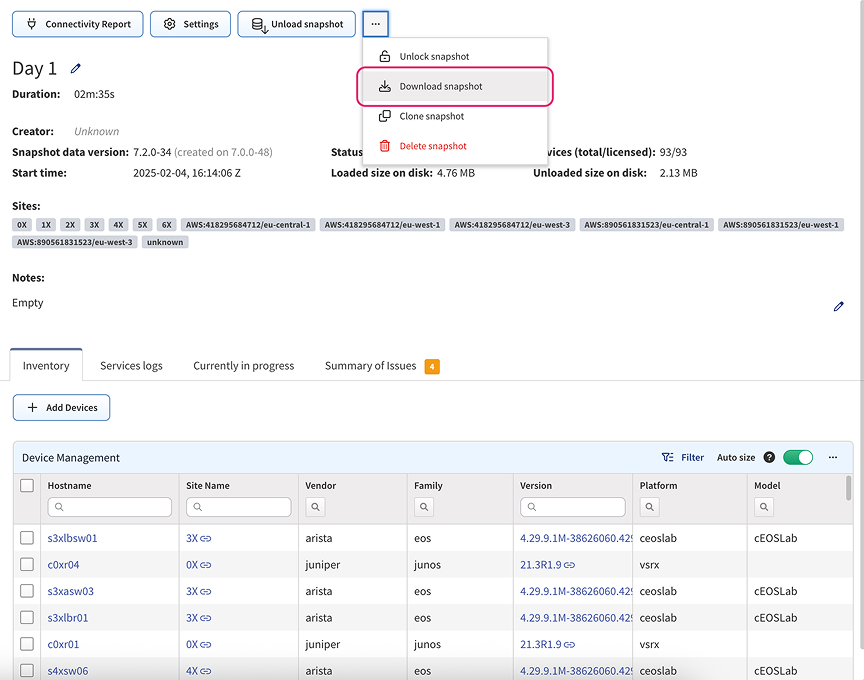
IP Fabric provides secure configuration backups to use in business continuity, network availability, and disaster recovery plans.
More on ISO 27001
Security Policy Validation
IP Fabric supplies key security information team that network teams need, giving a common language for network and security teams to understand the infrastructure through, ensuring proactivity, fast incident resolution (lower MTTR), and less friction between teams.
More on ISO 27001
Segmentation Validation
More on ISO 27001
End to End Analysis
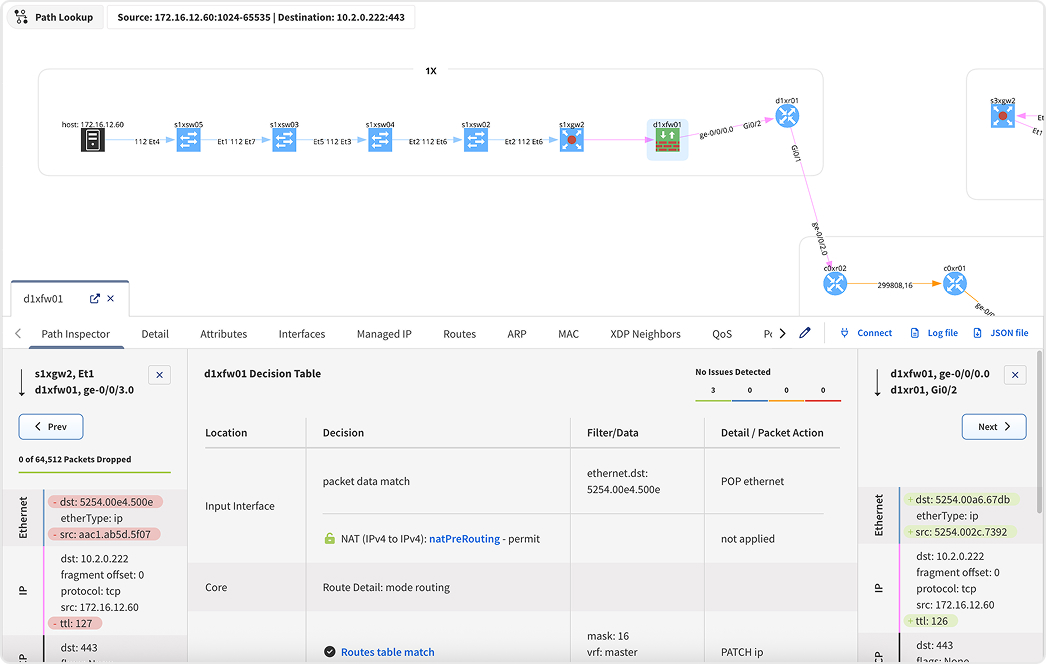
Automated End-to-End path visualization and analysis cuts out a repetitive manual data gathering process; saved path checks mean teams can quickly understand critical path status with every snapshot.
More on ISO 27001
Business Continuity Validation
Custom Dashboards for specific critical network segments or teams allow for a daily overview of business continuity, that you can securely share with a specific audience.
More on ISO 27001
Automated Incident Reponse
Use IP Fabric’s open REST API to trigger, and then validate, automated incident response.
More on ISO 27001
Automated Custom Reports
Most regulations give short windows for reporting on the state of the network; IP Fabric provides consumable reports with a click and the option to automate creation of custom network reports.
More on ISO 27001
Daily Discovery & Inventory
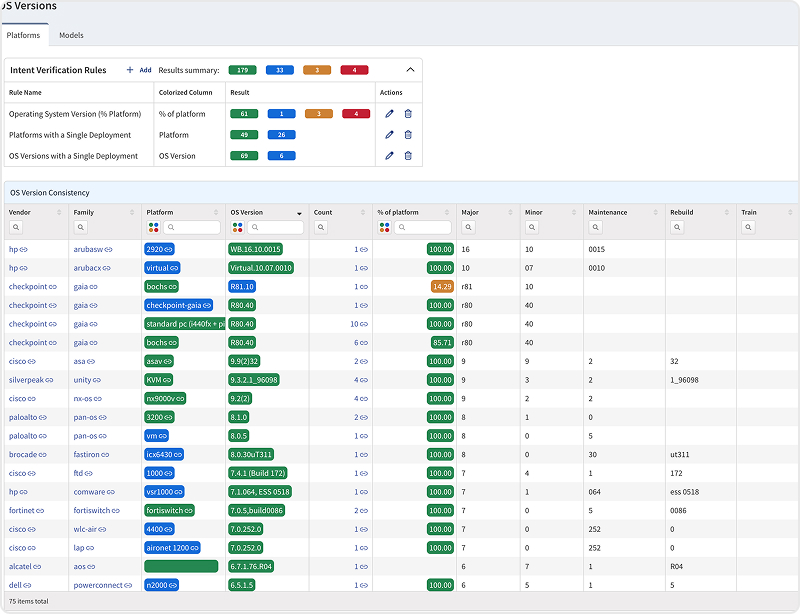
More on CIS
Lifecycle Management
IP Fabric provides detailed Lifecycle Maintenance Information with every snapshot – automating collection and normalization of this data from disparate vendors and technologies ensures accurate planning, reporting, and operation of critical networks.
More on CIS
Risk Identification
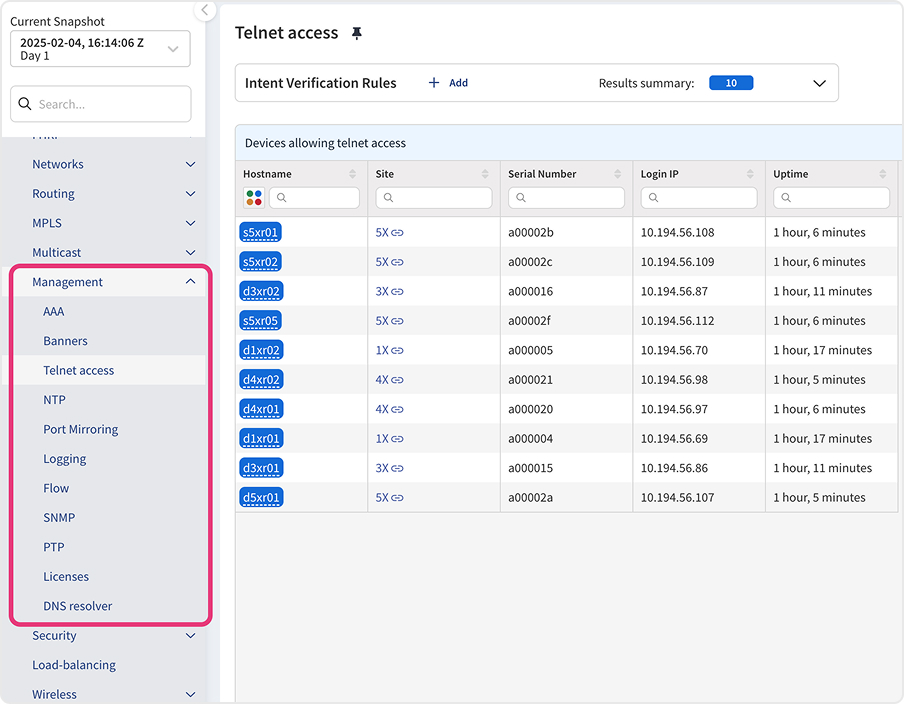
More on CIS
Configuration Backups
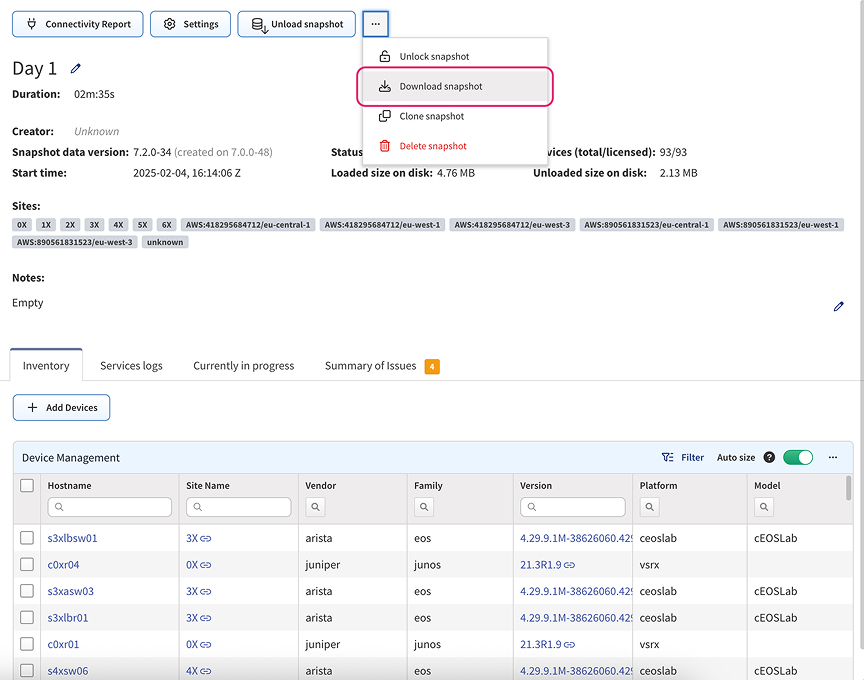
IP Fabric provides secure configuration backups to use in business continuity, network availability, and disaster recovery plans.
More on CIS
Security Policy Validation
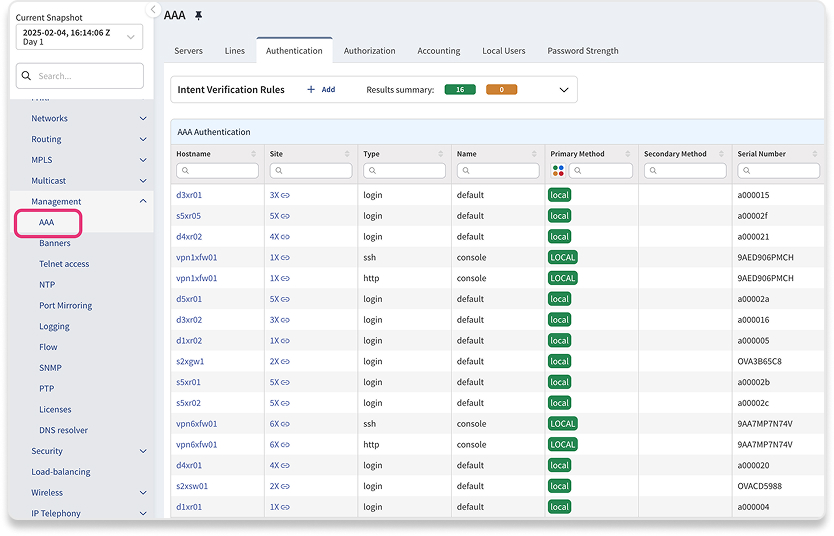
IP Fabric supplies key security information team that network teams need, giving a common language for network and security teams to understand the infrastructure through, ensuring proactivity, fast incident resolution (lower MTTR), and less friction between teams.
More on CIS
Segmentation Validation
More on CIS
End to End Analysis
Automated End-to-End path visualization and analysis cuts out a repetitive manual data gathering process; saved path checks mean teams can quickly understand critical path status with every snapshot.
More on CIS
Business Continuity Validation
Custom Dashboards for specific critical network segments or teams allow for a daily overview of business continuity, that you can securely share with a specific audience.
More on CIS
Automated Incident Reponse
Use IP Fabric’s open REST API to trigger, and then validate, automated incident response.
More on CIS
Automated Custom Reports
Most regulations give short windows for reporting on the state of the network; IP Fabric provides consumable reports with a click and the option to automate creation of custom network reports.